Barracuda SecureEdge ZTNA
NAC/ZTNA ZTNA
Barracuda SecureEdge is Barracuda's cloud-first SASE platform with an embedded ZTNA service ("SecureEdge Access") that provides identity- and device-centric access to private and SaaS apps, plus SWG, DNS filtering, and FWaaS, all managed centrally.
From a ZTNA point of view, it's positioned as a simpler, mid-market-friendly alternative to heavyweight enterprise ZTNA stacks, but still with enterprise-class security controls.
Overview
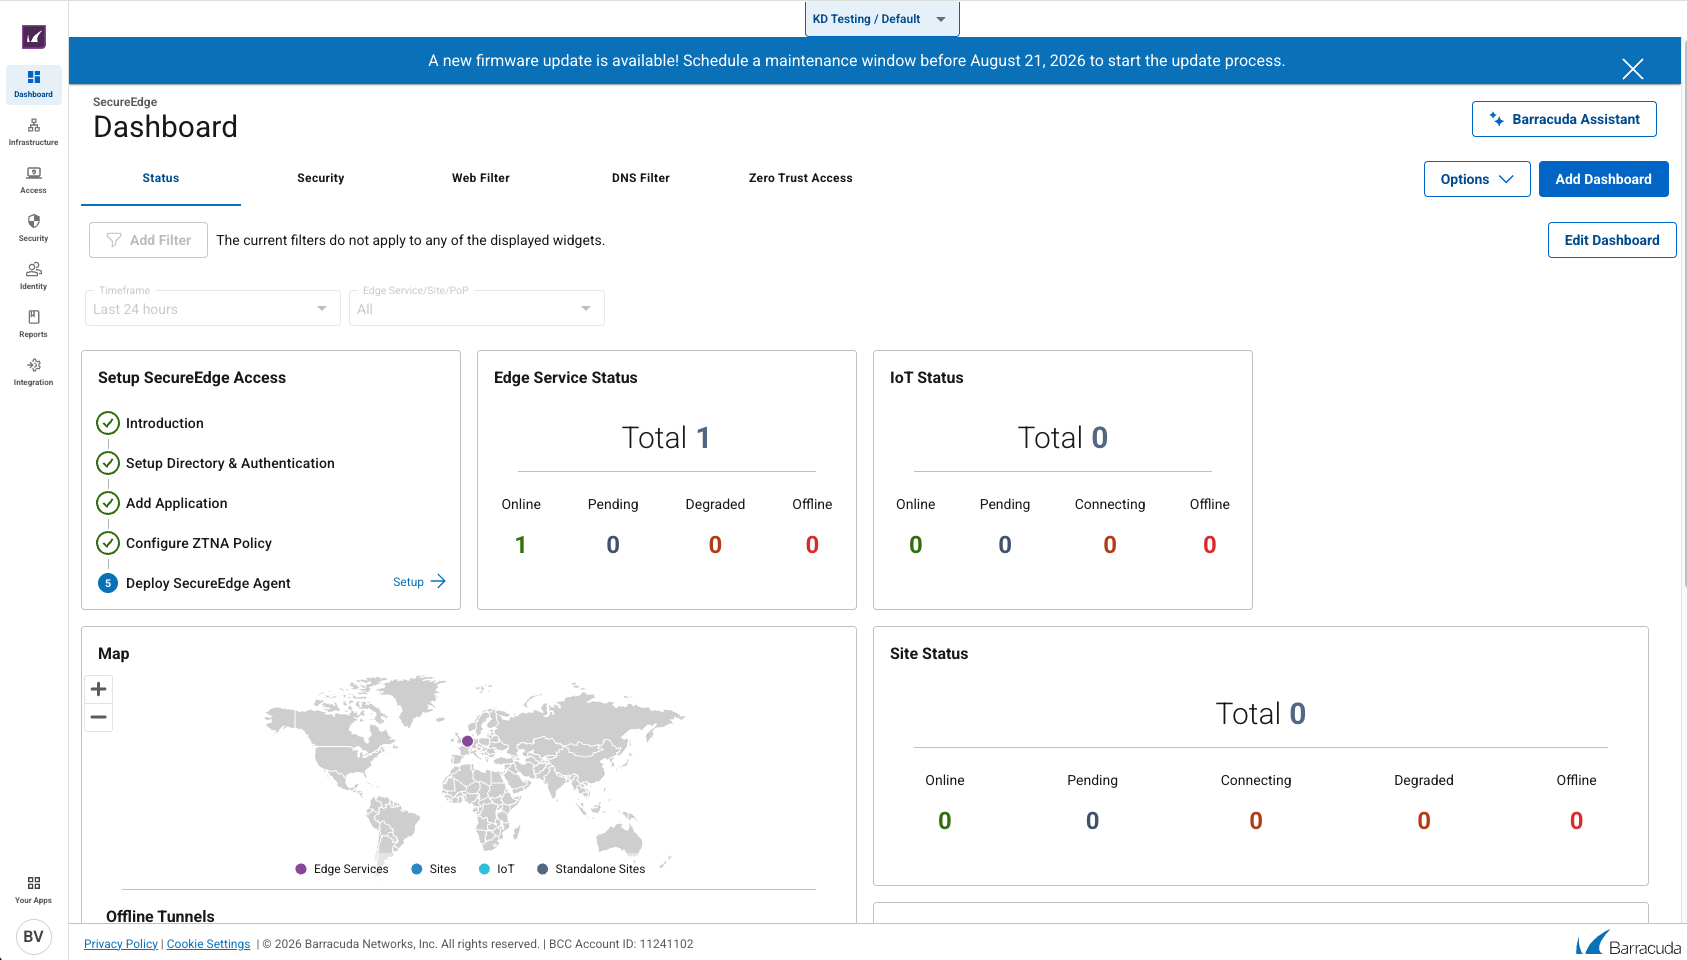
- SecureEdge is a cloud-delivered SASE platform that converges SD-WAN, next-gen firewall, Zero Trust Network Access, and Secure Web Gateway into a single service, aimed at both enterprises and MSPs.
- The ZTNA piece, branded "SecureEdge Access", has evolved into a broader Secure Service Edge (SSE) offering that unifies ZTNA, web security, DNS filtering, FWaaS, and DLP, delivered from a global multi-tenant SaaS platform with distributed PoPs
- Access is enforced at the application level rather than network level: users and devices connect via the SecureEdge Access Agent to defined private or SaaS applications, with least-privilege policies and continuous verification
From a ZTNA lens, think of SecureEdge as "Barracuda's unified agent + cloud control plane that replaces VPN and legacy hub-and-spoke firewall models with application-centric, identity driven access and inline security."
How to position
Target Customers
Mid-market and resource-constrained IT teams
Barracuda explicitly notes that many ZTNA tools were built for large enterprises and are too complex for smaller teams, and positions SecureEdge Access as a "simple yet powerful" ZTNA solution with an easy web UI and no hardware requirement.
Distributed/hybrid-work organizations
SecureEdge is marketed to support remote users, mobile users, and branch offices accessing apps from anywhere, with unified policies and consistent user experience whether remote or in-office.
Customers with many small sites and a large remote workforce (retail, manufacturing with branches, multi-site professional services, education) are prime candidates.
Cloud-first and Microsoft-centric environments
Barracuda has strong Azure and Microsoft 365 positioning; SecureEdge is listed as a cloud-first SASE platform that can extend security inspection and policy enforcement in the cloud, at the branch, or on the device, and is sold in government/enterprise marketplaces with explicit Microsoft 365 extension language.
Environments already standardized on Microsoft 365 and public cloud (especially Azure) are natural SecureEdge targets.
Existing Barracuda customers (Cloudgen Firewall, email security, etc)
SecureEdge can directly enroll Barracuda CloudGen Firewall appliances so that ZTNA policies and custom applications are sent down to those appliances from the SecureEdge control plane.
Organizations already using Barrcuda CloudGen Firewall or other Barracuda network/email security products are logical upsell candidates into SecureEdge as their "SASE/ZTNA overlay".
Easy-wins
VPN replacement/consolidation
SecureEdge explicitly positions ZTNA As a way to establish a Zero Trust model for secure access, granting least-privileged access to authorized apps without exposing the private network and improving remote access performance.
Any customer complaining about legacy VPN sprawl, split-tunnel complexity, or inconsistent remote access performance is a direct SecureEdge ZTNA opportunity
Rapid rollout of secure remote access
Remote users self-enroll the SecureEdge Access Agent from app stores, can use up to 10 devices per user simultaneously, and then get ZTNA and Secure Internet Access via the same client, which is attractive where IT wants fast rollout with minimal touch.
This is a quick win in mergers/acquisitions, contractor access scenarios, or "we need secure remote access by next quarter" projects.
Web security + ZTNA from one agent
The unified agent provides both ZTNA and web security (SWG, DNS filtering) as part of the SSE plans, which Barracuda sells as a single SaaS bundle (DNS access, full access plans, etc). Customers currently running separate cloud proxy/SWG and VPN/ZTNA agents are strong candidates to consolidate onto SecureEdge.
Cross-Sell Opportunities
CloudGen Firewall
Barracuda documentation shows that CloudGen Firewall units can be enrolled into SecureEdge, where ZTNA policies and custom applications are pushed into those firewalls and VPN connectivity is controlled from the cloud.
This is a natural motion: upgrade CloudGen Firewall customers to SecureEdge for global policy, ZTNA, and SSE while preserving their existing firewall investments
From Barracuda email protection to SecureEdge
Barracuda has a large email security installed base (Email Protection, Total Email Protection, etc) which provides cloud-based protection against phishing, malware, ransomware, and more.
You can position SecureEdge as the network access and web layer that complements email security by enforcing Zero Trust access to apps and inspecting web traffic for threats that email controls might redirect users to.
From standalone SD-WAN / MPLS to SecureEdge
SecureEdge uses SD-WAN capabilities, Auto-SD-WAN policies, and advanced packet-loss reduction to optimize application flow and allow customers to avoid expensive dedicated lines.
MPLS-heavy or "dumb" SD-WAN customers are good candidates to move to SecureEdge and simultaneously get ZTNA, SWG and FWaaS as part of the same platform.
Core Features
Zero Trust Network Access
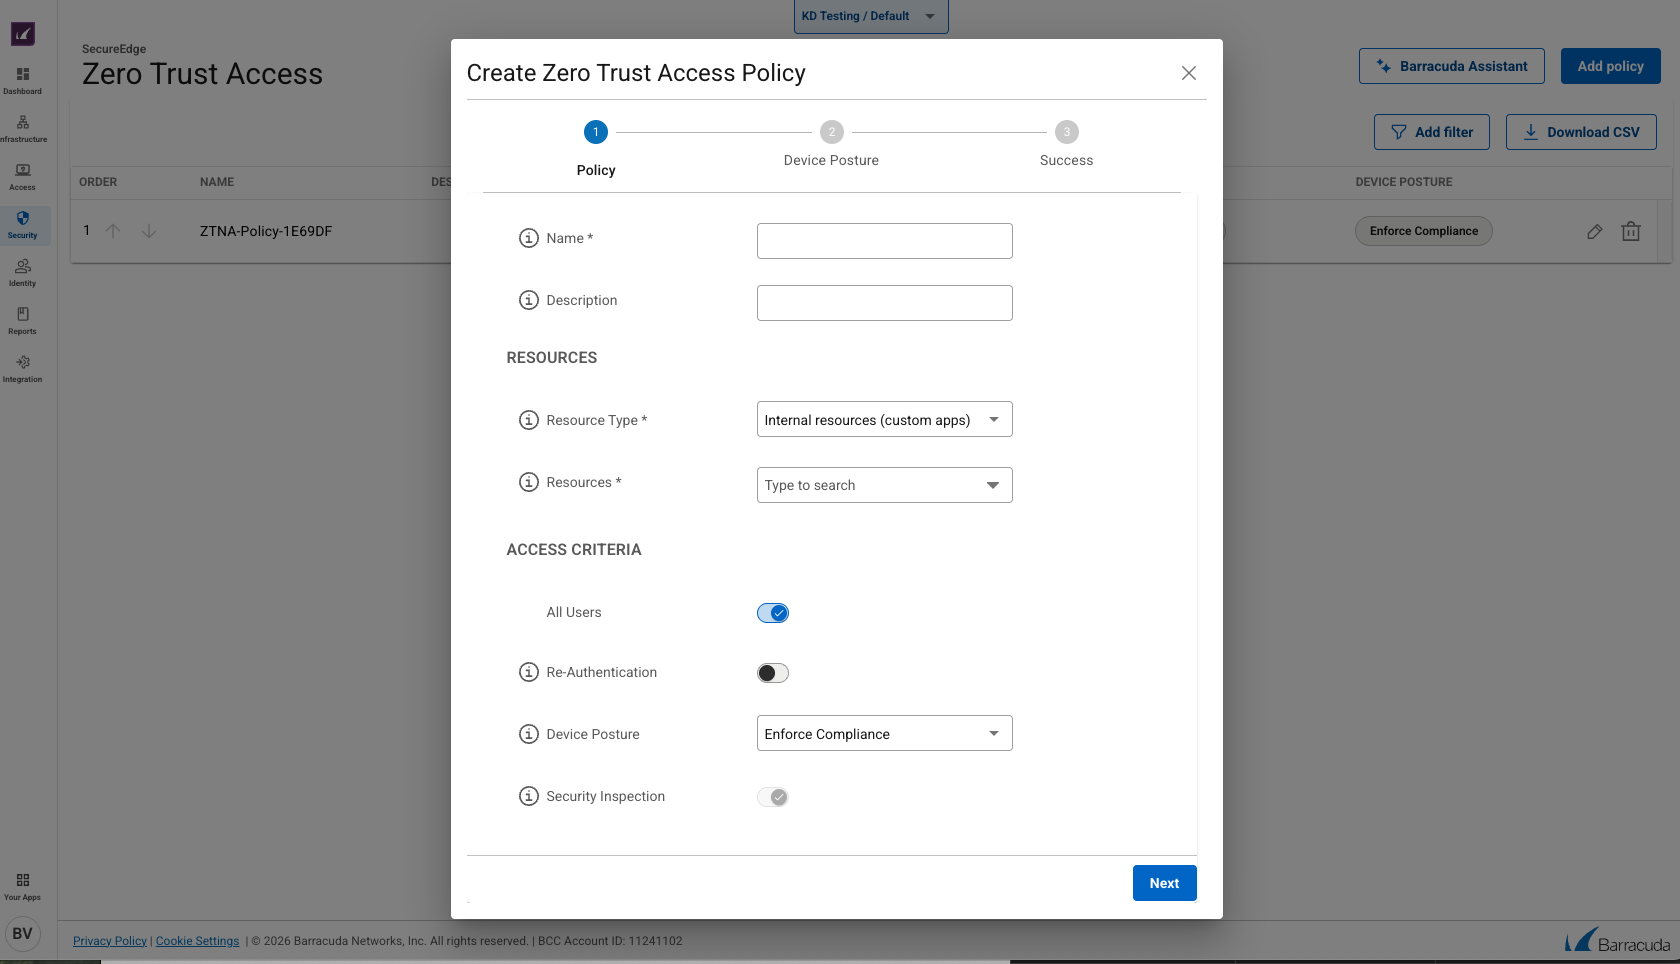
- SecureEdge enforces identity-based access, device posture checks, least-privilege policies, and continuous verification, aligning with core ZTNA principles
- Access is granted at the application level (any TCP/UDP-based app, including on-prem and public cloud via SD-WAN connectors) rather than giving full network access
- It supports secure third-party access, continuously checking device identity and security posture before and during sessions
Unified SSE / SASE services
- The SecureEdge Access service is a global, multi-tenant SaaS platform that unifies DNS filtering, ZTNA, FWaaS, and Secure Web Gateway: an AI-based web content filter and DLP are part of the SSE plans
- Barracuda positions SecureEdge as a cloud-first SASE solution providing Zero Trust Network Access, Firewall-as-a-Service, web security, and integrated Secure SD-WAN for office connectivity
SecureEdge Access Agent
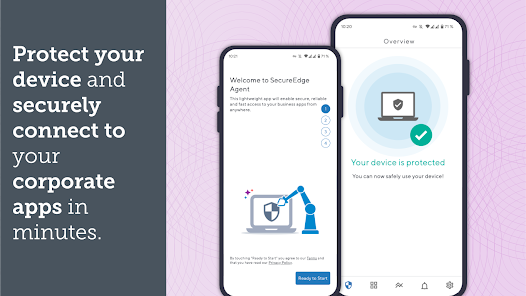
- The SecureEdge Access Agent provides the ZTNA and secure internet access endpoint, building TINA tunnels between teha agent and Edge services, and supporting multiple entry points (firewalls, Edge services, sites)
- It runs on Windows, macOS, iOS, Android and Linux, supports up to 10 simultaneous devices per user, and is described as tamper-proof across all platforms
- The agent integrates client-based and DNS-based web filtering, and automatically enrolls users with zero-touch self-enrollment workflows
Security inspection and threat protection
- SecureEdge Access uses Barracuda's proprietary TINA encryption protocol, which they emphasize as "never-compromised", ultra-stable and optimized with packet-loss reduction for high-performance encrypted tunnels
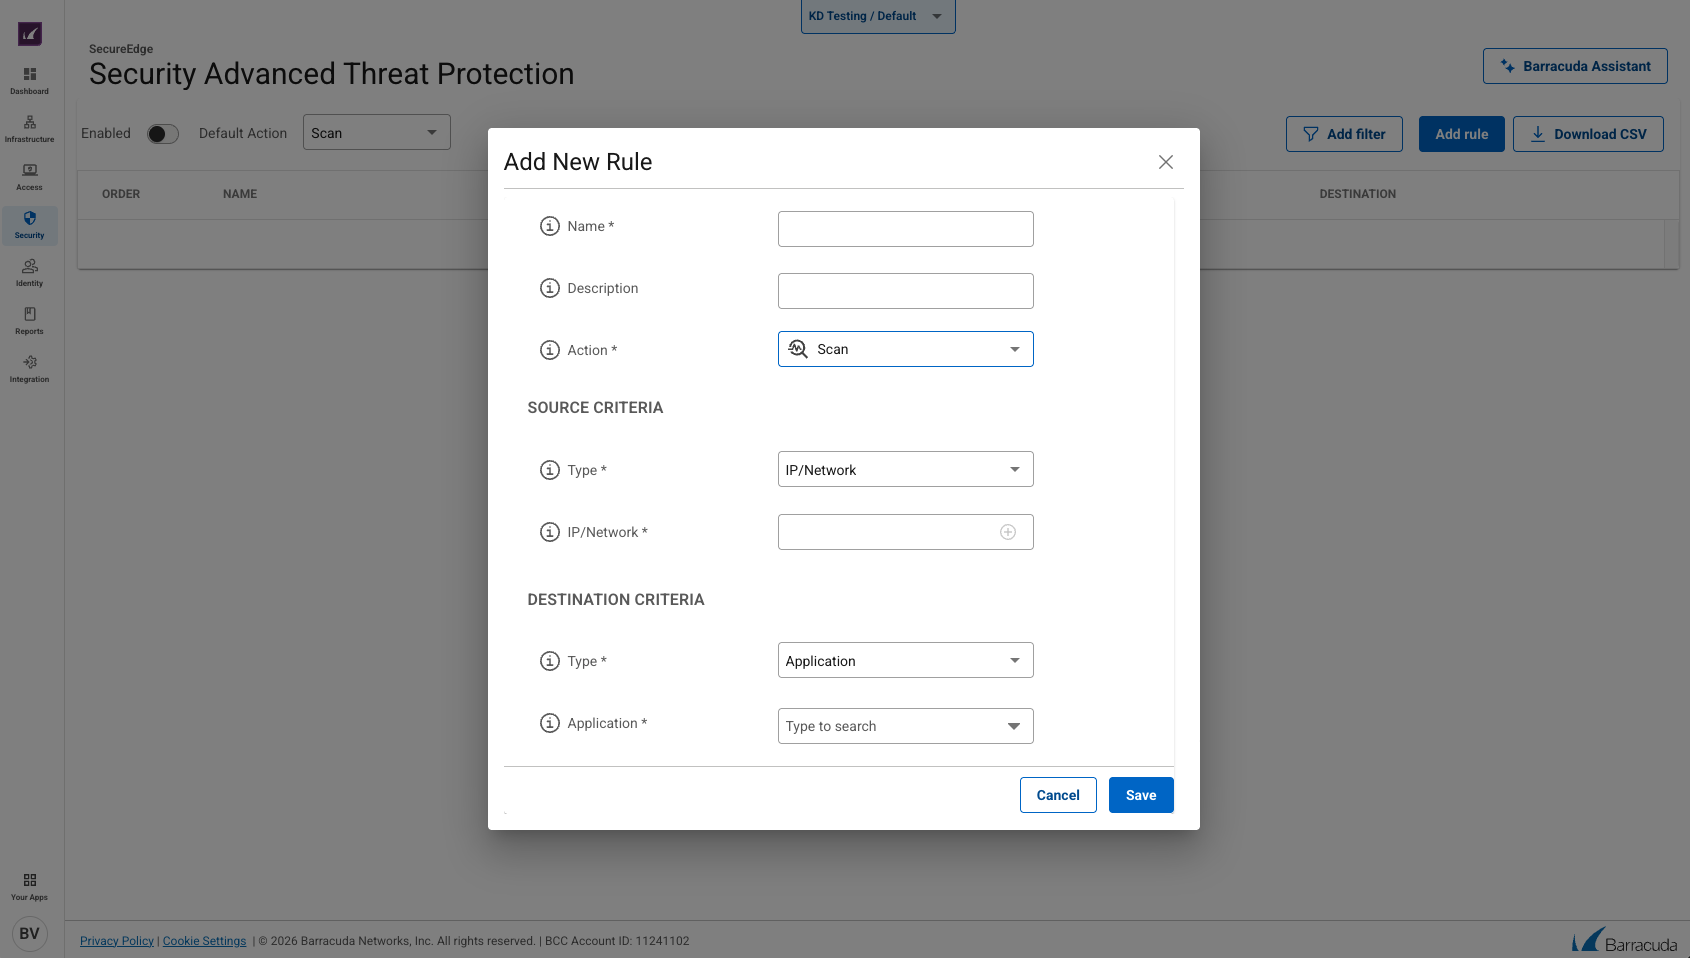
- It includes traffic inspection with Barracuda Advanced Threat Protection, including sandboxing and category-based web filtering to block malicious or suspicious sites and files, including zero-day threats
SD-WAN and connectivity
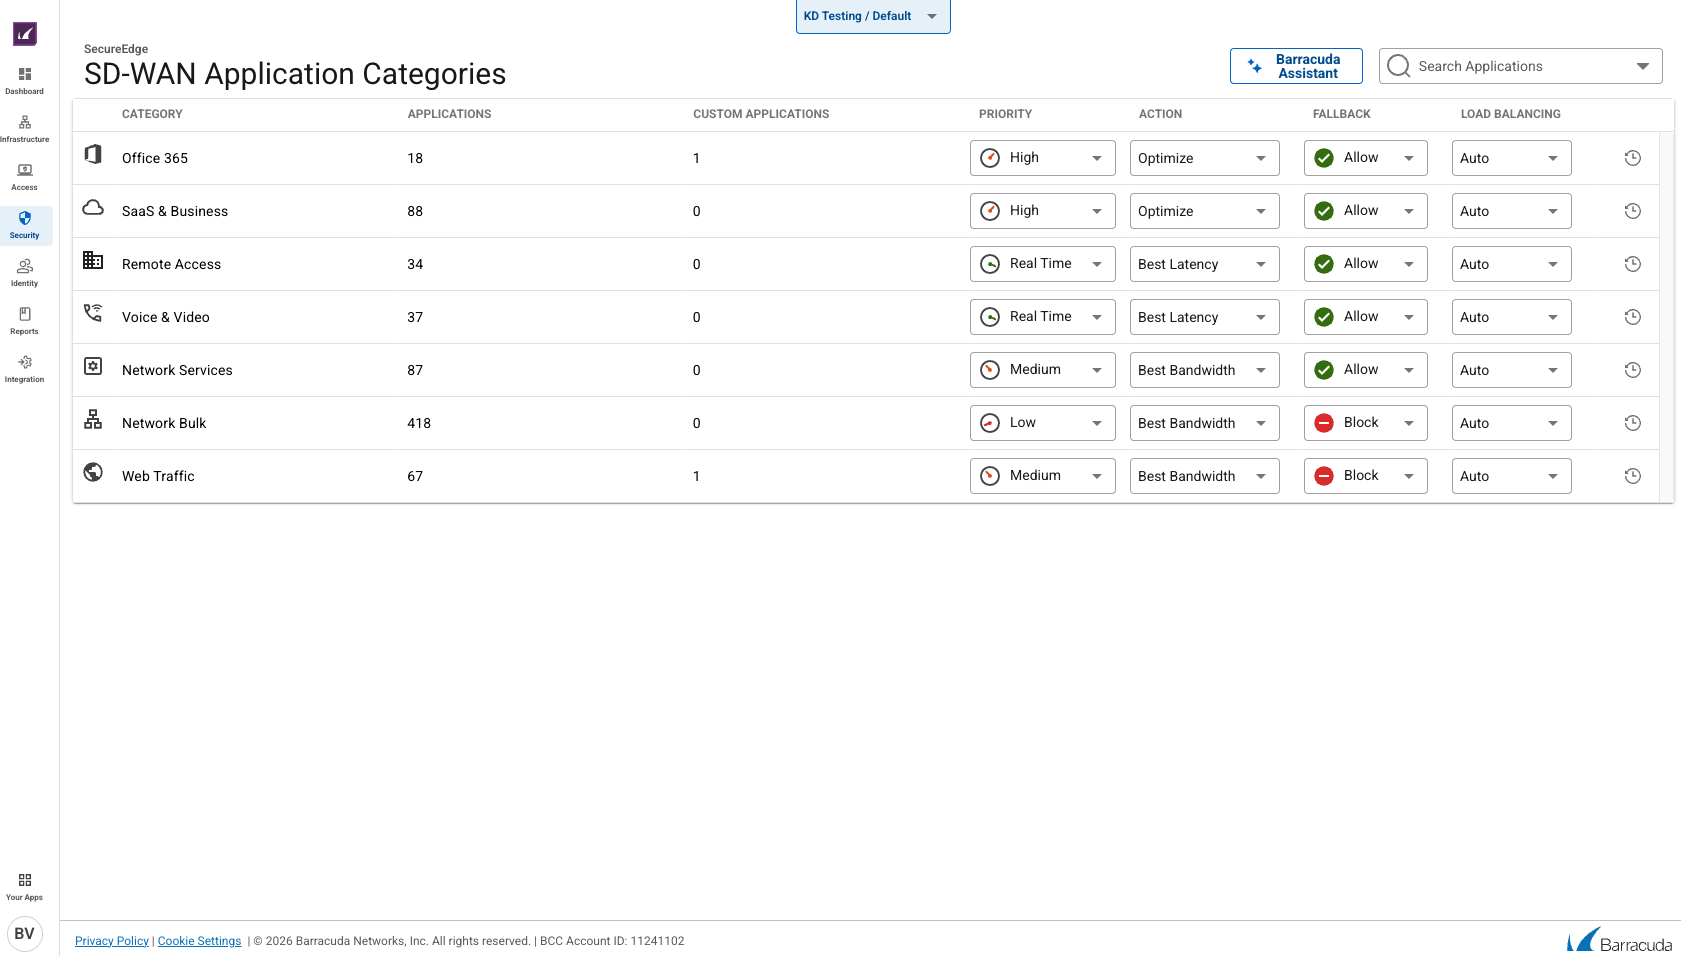
- Site devices (for branches/campuses) connect to SecureEdge via zero-touch deployment, automatically using all available uplinks and Auto-SD-WAN policies for thousands of applications
- SD-WAN functions include multi-uplink session balancing, provider selection, provider pinning, uplink health checks, and WAN types ranging from static/dynamic IP to ExpressRoute and LTE
- For remote users, SD-WAN optimizations such as forward error correction and packet-loss reduction are appliad across tunnels, improving performance even over congested links
Centralized policy and management
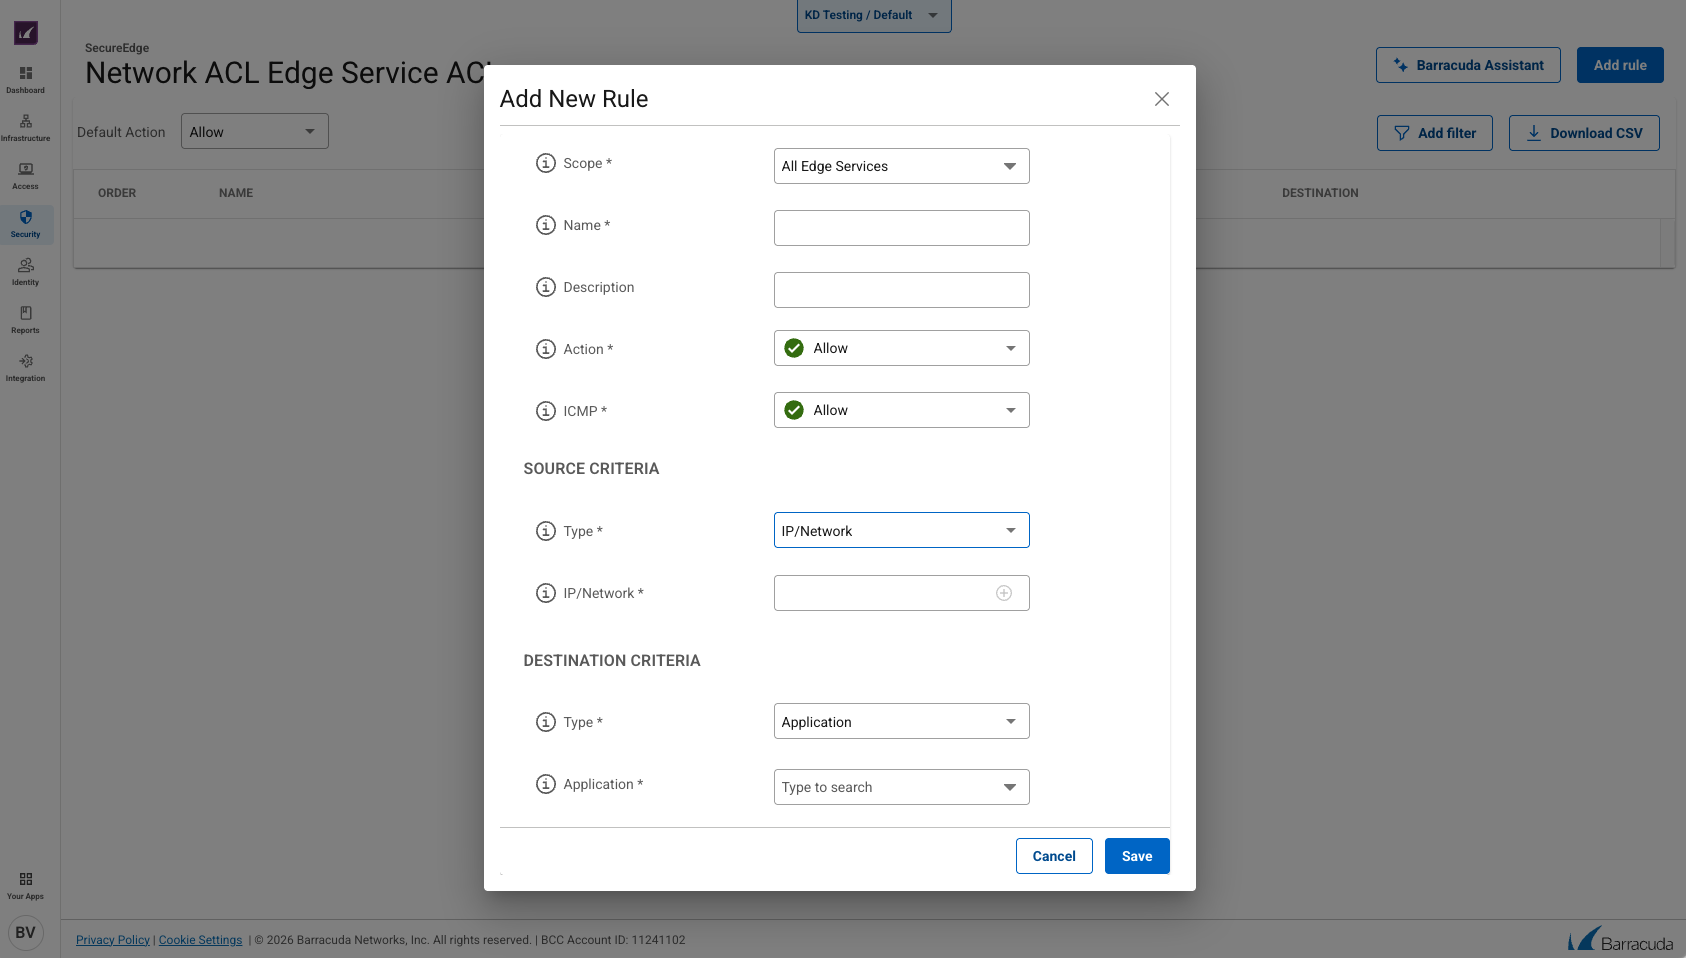
- SecureEdge is managed via a cloud console that centralizes policy enforcement for ZTNA, web security, and SD-WAN, with role-based access and an "application catalog" for predefined apps
- "Once-only intent-based management" allows you to define private applications once; those definitions are then shared across security, SD-WAN and ZTNA policy definitions, with networking and routing handled automatically
- The platform offers reporting and detailed log visibility with at least 30-day retention built in, supporting compliance and audit need.
Identity, SSO, and directory integration
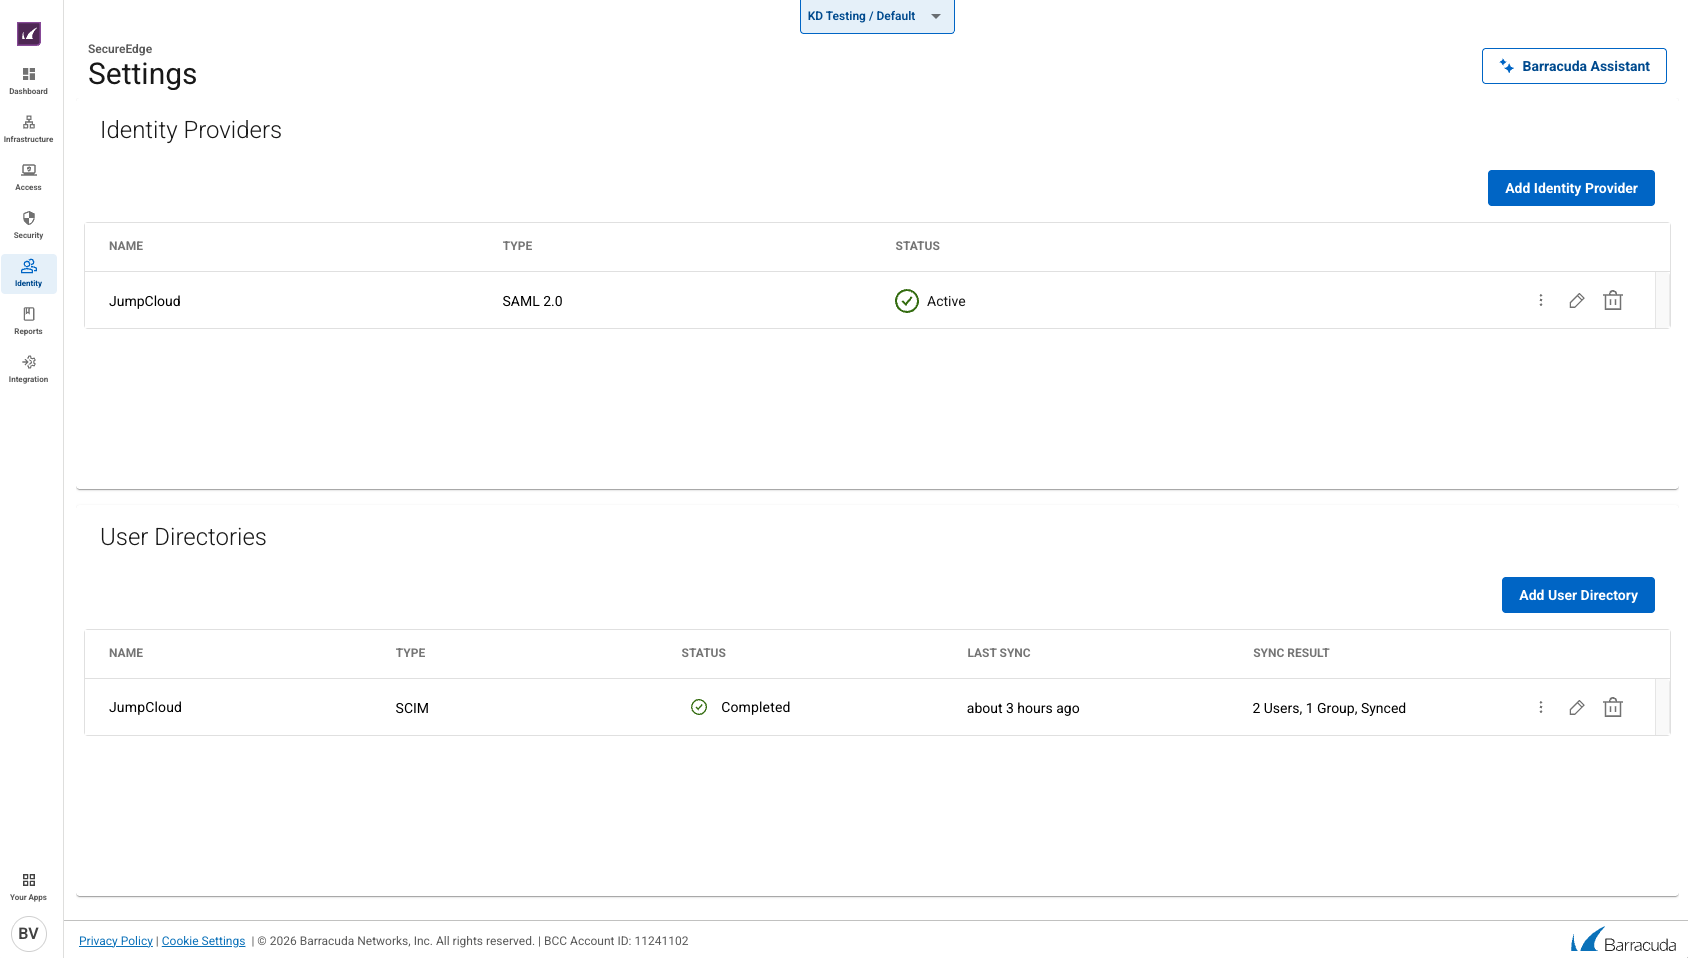
- SecureEdge Access integrates with Microsoft Entra ID, Google Workspace, Okta, other SAML-compatible IdPs, OpenID Connect, and classic Active Directory, and supports SCIM for automated provisioning
- Multiple identity providers and suer directories can be configured concurrently, enabling complex hybrid identity scenarios.
Feature Overview
- Access control model: Identity-based access with integrated role-based permissions; access is defined at the application level (any TCP/UDP app, on-prem or cloud) and follows least-privilege principles
- Device posture and security: Integrated device health checks based on ZTNA policy requirements verify device state before granting access; tamper-proof agent and continuous device identity checks for remote and third-party users
- Connectivity & performance: TINA-based tunnels between agent, Edge Services, and sites; multi-access-point capability, forward error correction, packet-loss reduction, and Auto-SD-WAN policies for thousands of apps to optimize user experience
- SSE/inline security: Unified SSE service provides DNS filtering, ZTNA, FWaaS, SWG, DLP, AI-based content filtering, TLS inspection, IPS, and advanced malware sandboxing for user and site traffic
- Deployment models: Fully managed SaaS with global PoPs; deployment options include Barracuda-hosted SaaS, private deployment, and integration with site appliances and CloudGen Firewalls via zero-touch enrollment
- Endpoint coverage: SecureEdge Access Agent supports Windows, macOS, iOS, Android and Linux, with up to 10 devices per user; remote users self-enroll from app stores
- Identity & SSO: SSO via Entra ID, Google Workspace, Okta, any SAML/OIDC IdP, plus AD; SCIM support for automated provisioning; multiple IdPs/user directories can be used in parallel
- Management & analytics: Central cloud console with intent-based policy management, application catalog, reporting, and log visibility (30-day retention), plus integration of CloudGen Firewall units for unified ZTNA policy distribution
- Use-case coverage: Secure remote workforce (ZTNA and SIA via one agent), secure branch connectivity with SD-WAN and FWaaS, secure IoT/ICS access, and secure third-party access scenarios