JumpCloud Cloud RADIUS
NAC/ZTNANAC
Overview
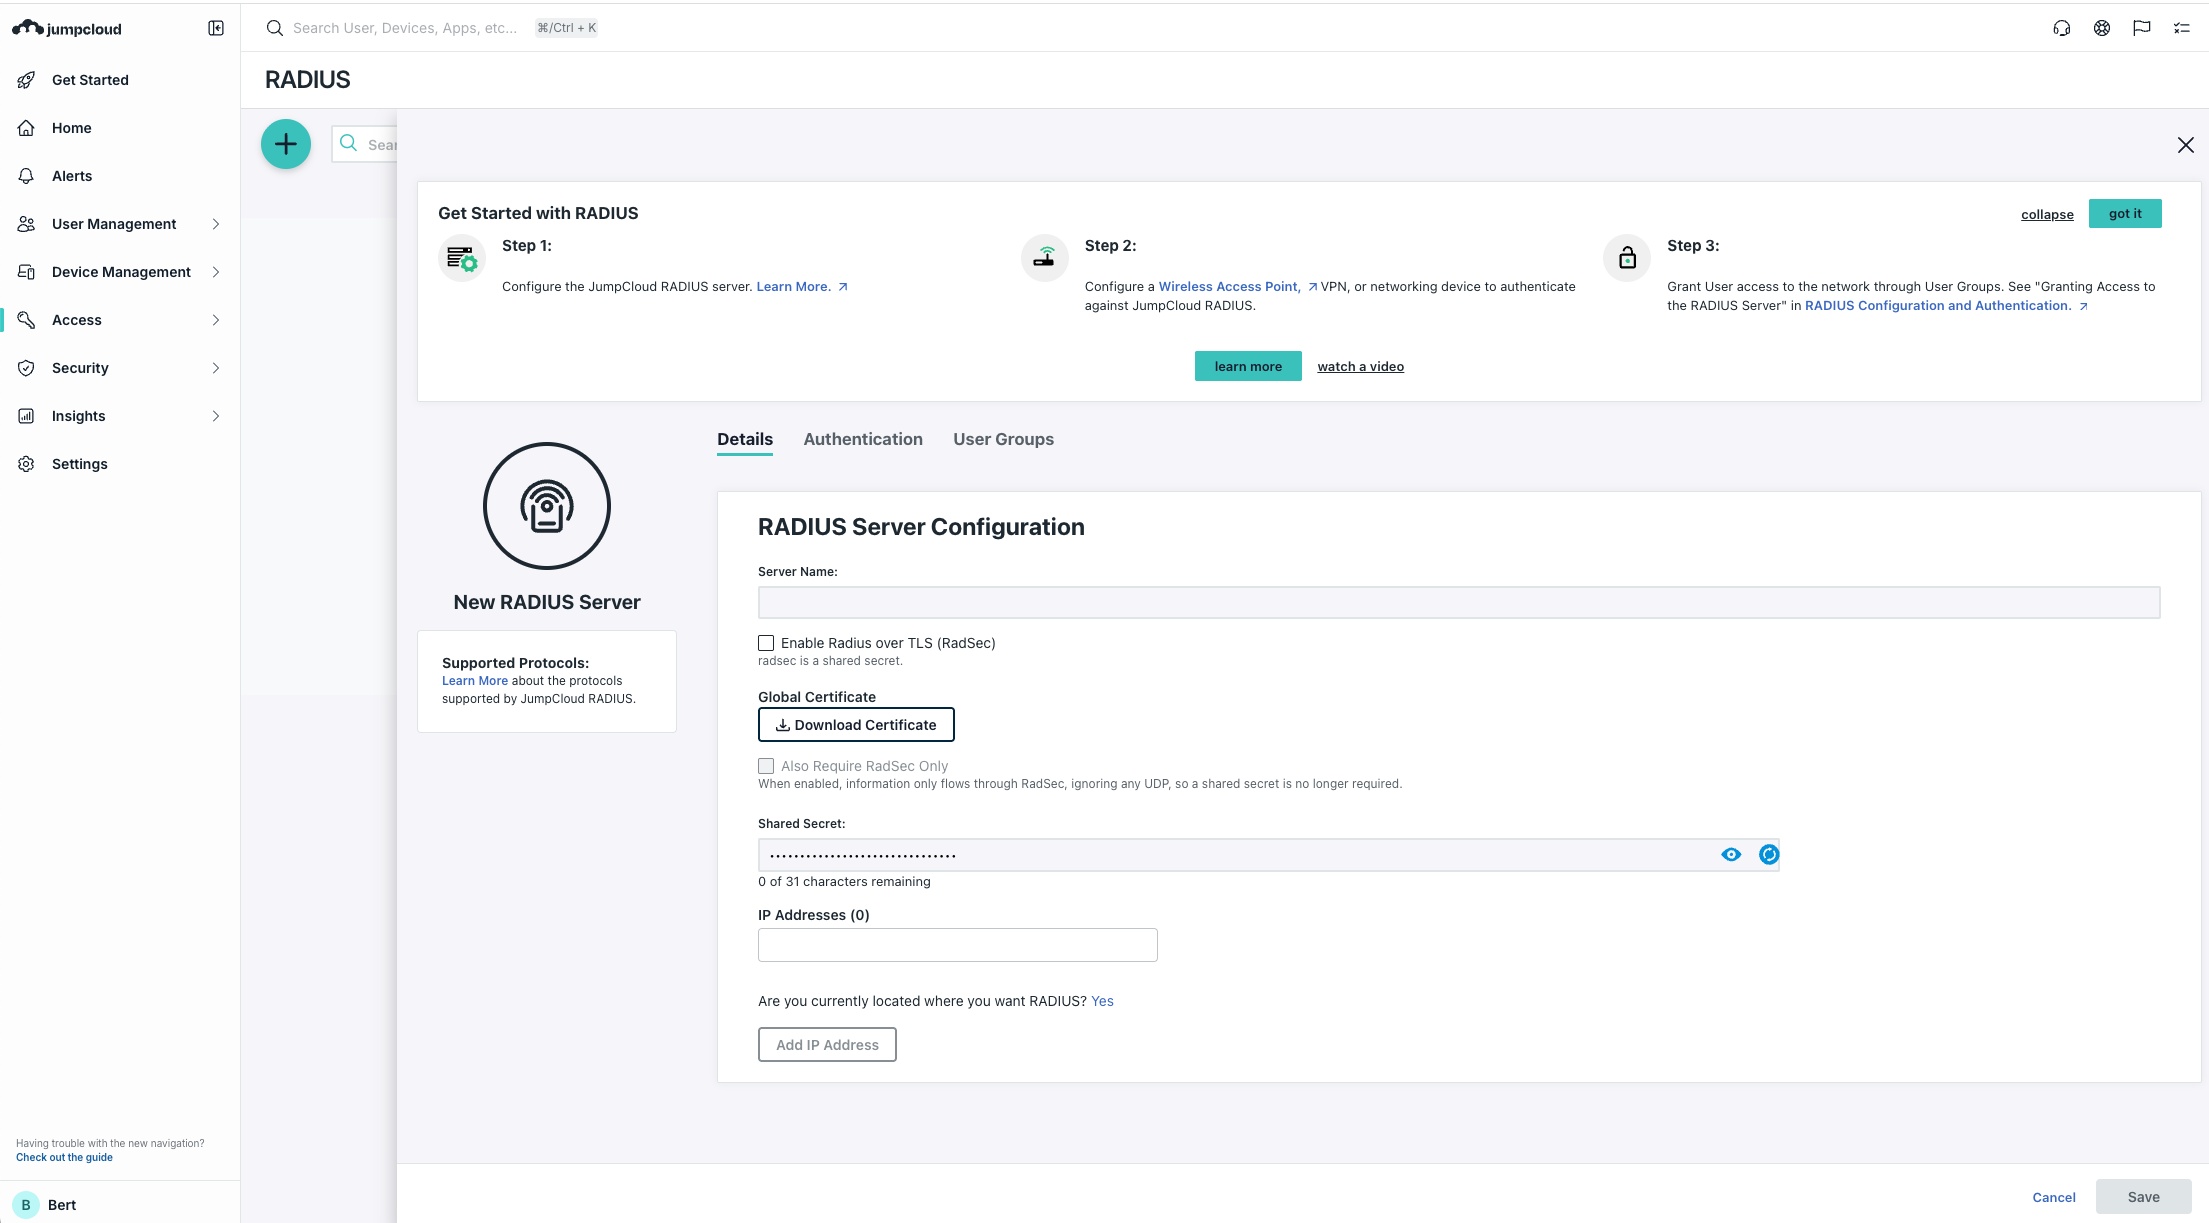
JumpCloud Cloud RADIUS is a fully managed RADIUS-as-a-Service (RaaS) offering embedded within the JumpCloud Open Directory Platform. It eliminates the need for on-premises RADIUS server hardware (such as Microsoft Windows Server NPS or FreeRADIUS) by providing pre-built, pre-configured, and scalable cloud-hosted RADIUS servers. Organisations simply point their wireless access points (WAPs), switches, or VPN concentrators to JumpCloud's RADIUS server IP addresses and authenticate users against the JumpCloud cloud directory, or optionally delegate authentication to Microsoft Entra ID
Cloud RADIUS is not a standalone product; it is a native capability of the JumpCloud directory platform (available from the Platform tier onwards). This means RADIUS authentication inherits the full user lifecycle, group management, MFA, conditional access, and device trust capabilities of JumpCloud without bolting on separate infrastructure.
How to position
JumpCloud Cloud RADIUS is designed primarily for small and medium-sized enterprises (SMEs) and mid-market organisations that:
- Lack the resources or appetite to maintain on-premises RADIUS infrastructure (Windows NPS, FreeRADIUS)
- Already use or are evaluating JumpCloud as their core directory/IdP
- Operate in a cloud-first or hybrid-cloud model with no on-prem Active Directory dependency
- Need to secure WiFi and/or VPN access with individual user credentials instead of shared PSKs
- Require VLAN-based network segmentation for compliance but find traditional RADIUS setups too complex
The easiest wins when positioning JumpCloud Cloud RADIUS:
- Existing JumpCloud customers not yet using RADIUS: Cloud RADIUS is included in the Platform tier at no additional per-module cost. It is a pure upsell within the existing platform
- Organisations still using shared WiFi PSKs: The jump from WPA2-Personal to WPA2-Enterprise with individual credentials is a major security uplift with minimal effort
- Companies replacing Windows NPS: Organisations migrating away from Windows Server / Active Directory lose their NPS RADIUS capability. JumpCloud provides a direct cloud replacement
- MSP-managed SMBs: MSPs using JumpCloud's multi-tenant platform can roll out RADIUS per client with minimal overhead
- Remote/Hybrid offices: Offices with dynamic public IPs can update the RADIUS config via API; VPN authentication via RADIUS+MFA is a quick security win.
Core Features
- AnyCast Routing: RADIUS requests are automatically routed to the nearest JumpCloud RADIUS server for low-latency authentication. Dedicated EU IP addresses are available for EU-tenant organisations
- Port 1812/UDP: Standard RADIUS authentication port. Accounting (port 1813) is not supported
- Public IPv4 only: Each public IP can only be registered once per RADIUS server instance. IPv6 is not supported
- RadSec support: JumpCloud supports RADIUS over TLS (RadSec) for encrypted RADIUS transport.
- One server per network: Each RADIUS server instance controls a single network. Multiple SSIDs require multiple RADIUS server instances.
Supported EAP/Authentication Protocols
All protocols are available simultaneously; the client device selects the protocol during connection:
| Protocol | Inner Auth | MFA Support | Notes |
|---|---|---|---|
| EAP-PEAP (PEAPv0) | MSCHAPv2 | Push | Most common; easiest client setup |
| EAP-TTLS | PAP | TOTP + Push | Requires client-side Wi-Fi profile; supports Anonymous Outer Identity |
| EAP-TLS | Certificate (mTLS) | None | Passwordless; requires certificate deployment on clients |
| EAP-MSCHAPv2 | — | Push | Shared key encryption variant |
| MSCHAPv2 | — | Push | Non-EAP variant; often used by VPN devices |
| PAP | — | TOTP + Push | Weak encryption; not recommended but supported for legacy devices |
- MFA for RADIUS can be enabled per RADIUS server instance and supports TOTP (via authenticator apps like JumpCloud Protect, Microsoft Authenticator, Google Authenticator) and Push notifications (via JumpCloud Protect). MFA is recommended for VPN servers; it is generally not recommended for WiFi due to user experience friction
- Dynamic VLAN Assignment: VLAN tagging is configured through RADIUS Reply Attributes on JumpCloud User Groups. When a user authenticates, JumpCloud returns the following attributes in the Access-Accept message:
Tunnel-Type= VLANTunnel-Medium-Type= IEEE-802Tunnel-Private-Group-ID= VLAN ID This enables per-group network segmentation without any on-prem RADIUS server. Attributes are configured in the Admin Portal under User Groups --> RADIUS tab, or programmatically via the JumpCloud PowerShell Module or REST API. Up to 50 reply attributes per user group are supported.
User & Group-Based Access Control
- RADIUS server instances are bound to User Groups. Only users in an assigned group can authenticate to that RADIUS server
- Access is provisioned or revoked by adding/removing users from groups: instantly effective
- JumpCloud supports attribute-based access control (ABAC) and can automatically adjust group memberships based on user attribute changes or HR-triggered events
- Temporary access for vendors, contractors, or travelling employees is straightforward: create a user, assign to a group, remove when done.
NAC Context
From a Network Access Control (NAC) perspective, JumpCloud Cloud RADIUS serves as the authentication and authorisation back-end for 802.1X-secured networks. It covers three primary use-cases:
- WLAN: Wireless Access Points (WPA2/WPA3 Enterprise)
- Switches: 802.1X port-based NAC on managed switches
- VPN: VPN concentrators or gateways
Feature Overview
- Managed RADIUS Servers: Pre-built, fully managed, scalable.
- AnyCast Routing: Automatic routing to nearest RADIUS server; dedicated EU endpoints available
- RadSec (RADIUS over TLS): Encrypted RADIUS transport supported
- Authentication: Password JumpCloud credentials (username/email + password)
- Authentication: CBA (EAP-TLS): Bring Your Own Certificates; X.509 validation against imported CA trust chain
- Authentication: Delegated (Entra ID): Entra ID as IdP with JumpCloud RADIUS as authentication frontend
- EAP Protocols: EAP-PEAP/MSCHAPv2, EAP-TTLS/PAP, EAP-TLS, EAP-MSCHAPv2, MSCHAPv2, PAP
- TLS Version: TLSv1.2 or later required
- MFA (TOTP+Push): Per-server toggle; supports JumpCloud Protect push and TOTP apps
- Dynamic VLAN Assignment: Per-group RADIUS Reply Attributes (Tunnel-type, Tunnel-Medium-Type, Tunnel-Private-Group-Id)
- Custom Reply Attributes: Up to 50 attributes per user group; any valid FreeRADIUS dictionary attribute supported
- User Group Binding: RADIUS servers bound to User Groups for fine-grained access control
- Shared Secret: Auto-generated complex shared secrets for WAP/server authentication
- Public IP Validation: Requests validated against registered public IP of the network device
- Certificate Trust: Server certificate for client-side server validation
- Anonymous Outer Identity: Supported with EAP-TTLS profiles to obscure username in initial Access-Request
- API & PowerShell Module: Full RADIUS management via REST API and JumpCloud PowerShell Module
- Conditional Access: Platform Prime: device trust, IP/location conditions, disk encryption checks
- User Lifecycle Automation: Automatic group membership changes on attribute updates or HR termination events