Extreme Platform ONE Security
NAC/ZTNANAC
Overview
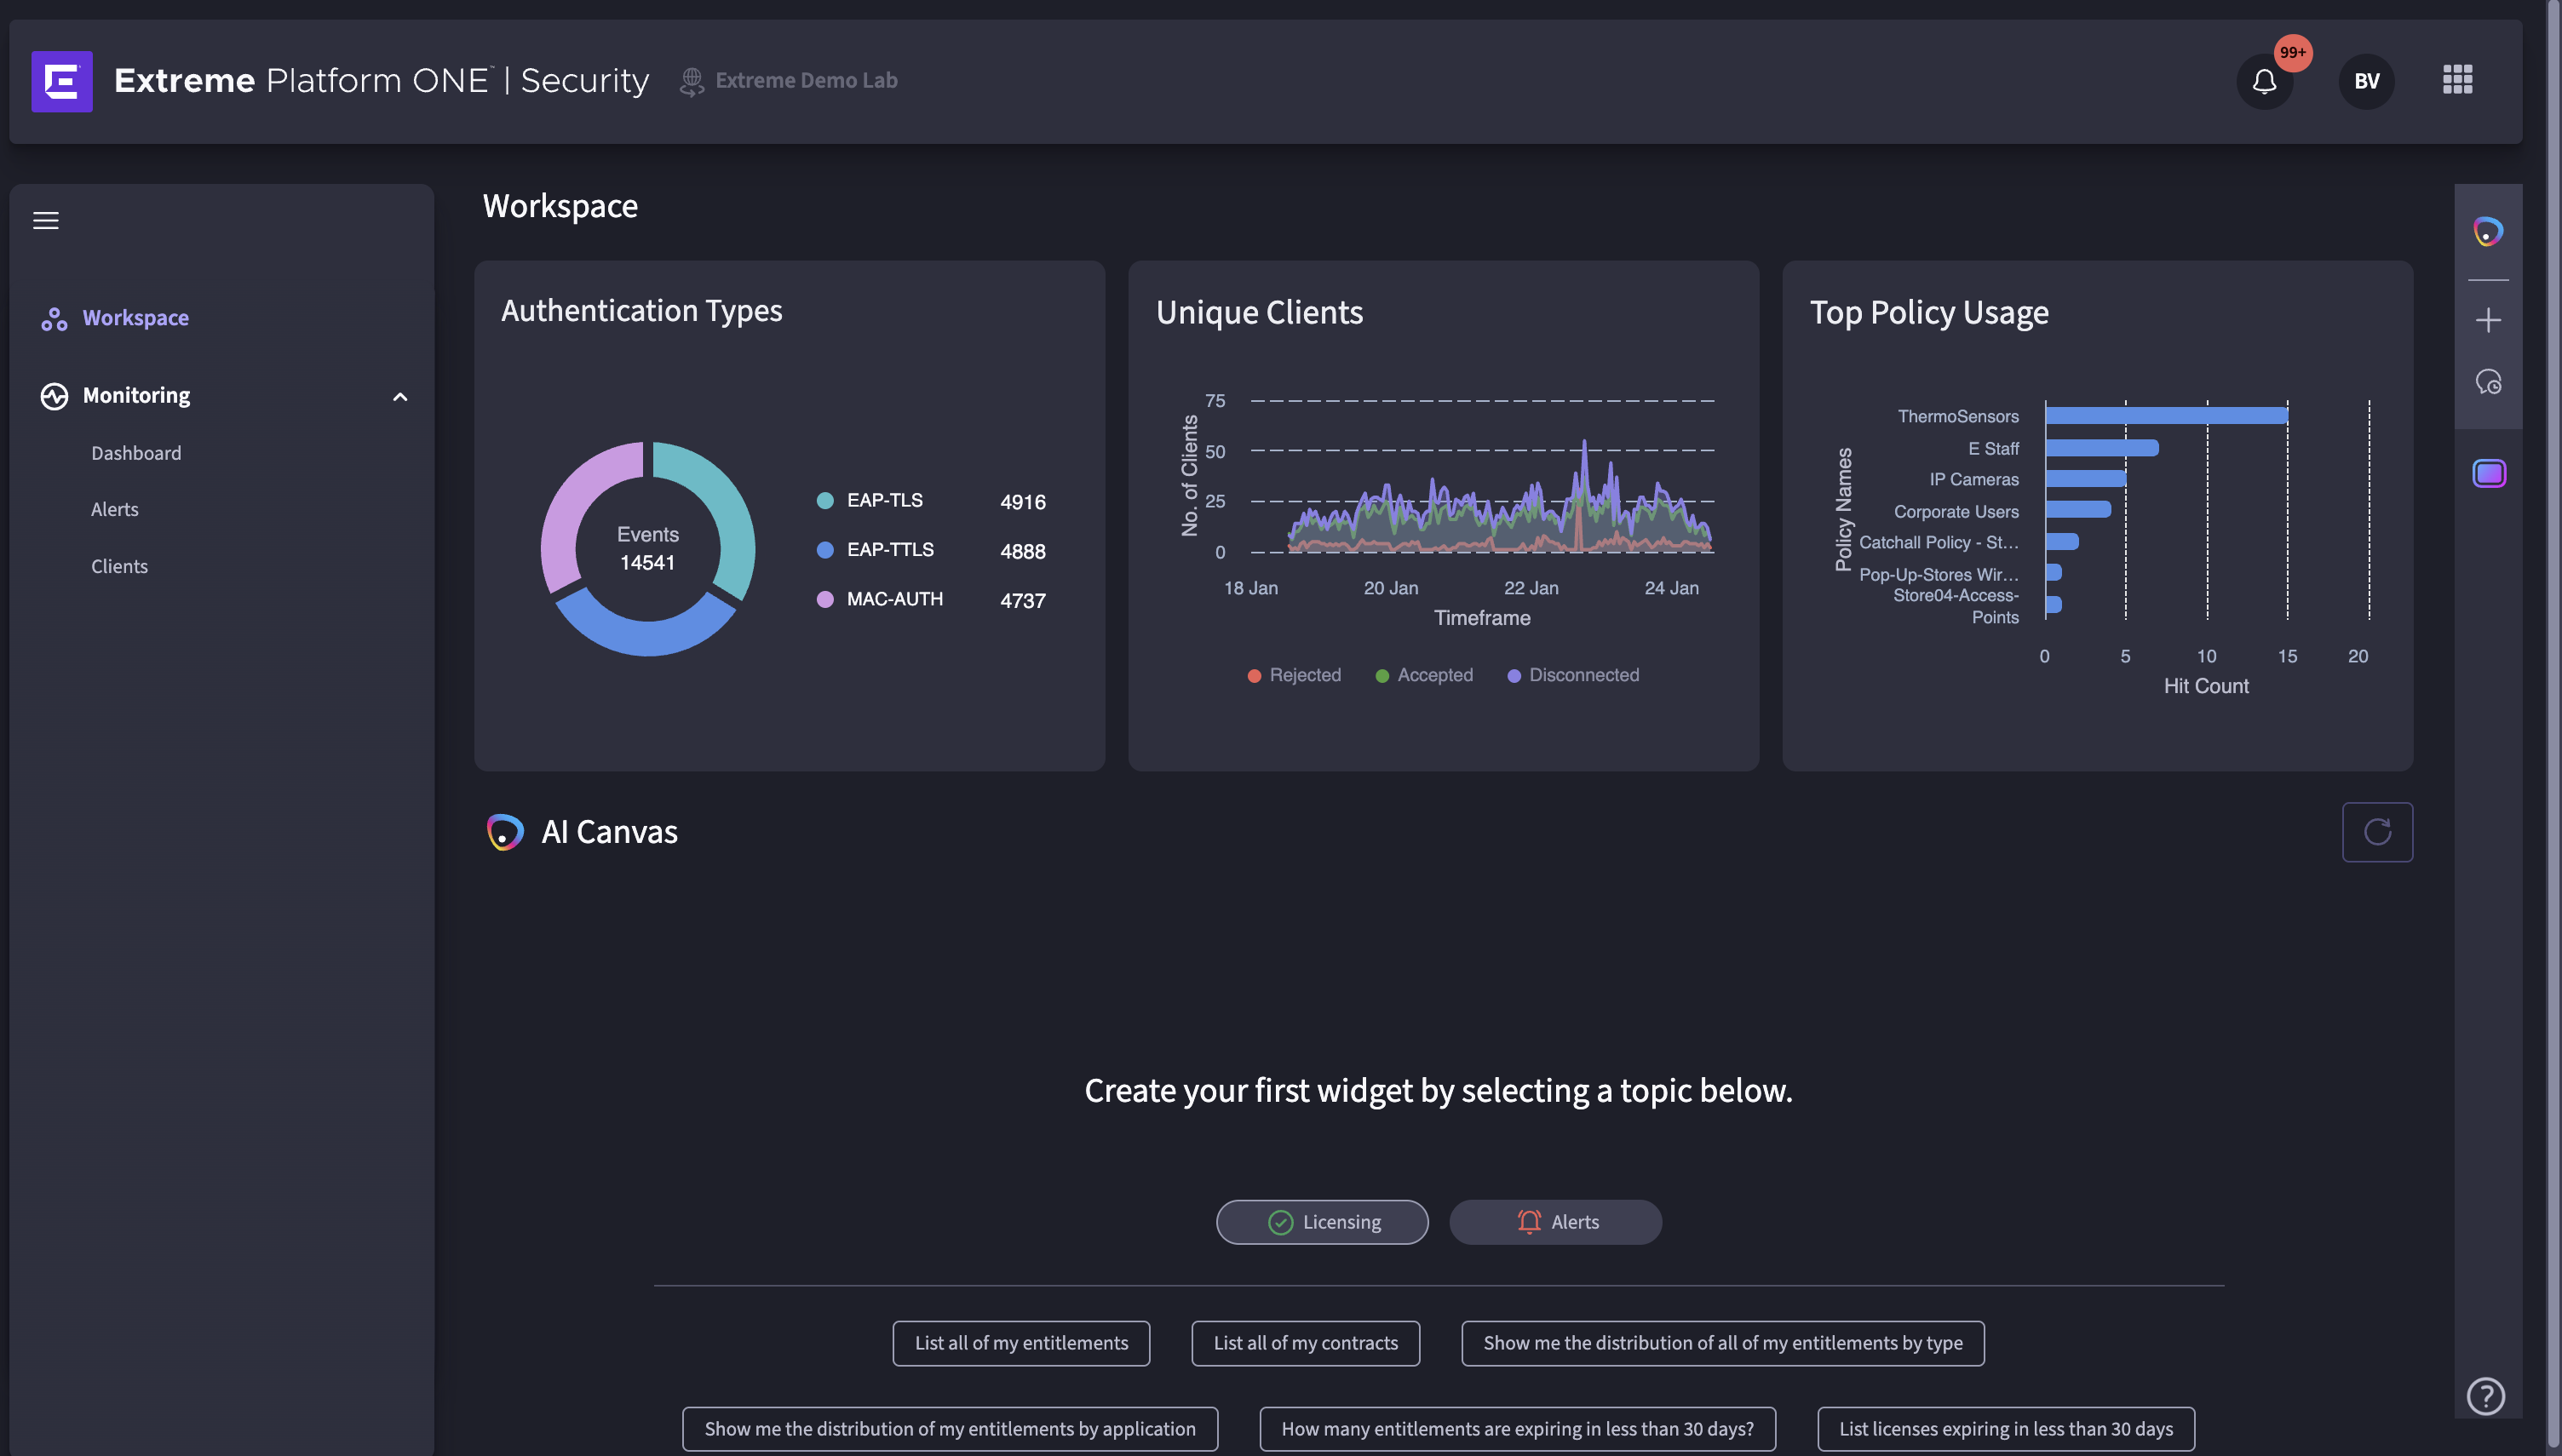
Extreme Platform ONE Security represents Extreme Networks' ambitious response to the converged networking and security demands of modern enterprises. Unlike competitors offering point solutions, Extreme has integrated network access control (NAC) and zero-trust network access (ZTNA) into a unified policy engine within a larger platform that manages wired fabric networks, wireless access points, and cloud security orchestration: all powered by conversational, multimodal AI
The differentiator is not incremental: Platform ONE Security unifies what competitors sell as separate products (NAC appliance, ZTNA gateway, Fabric management, wireless management). A single policy engine now enforces identity-based access across campus networks (Extreme Fabric), wireless (Universal APs), remote users (ZTNA with Service Connectors) and applications (private and IaaS). All driven by natural language policy creation through AI Expert, which allows IT teams to write policies conversationally (e.g. "Give Engineering access to the ERP system only from corporate offices between 8AM and 6PM") without mastering complex syntax.
The platform integrates seamlessly with leading identity providers (Microsoft Entra ID, Okta, Google Workspace) and mobile device management solutions (Microsoft Intune) enabling guided setup and automatic policy enforcement across Extreme's wired, wireless, and fabric infrastructure. This architectural simplicity, combined with a cloud-first subscription model that includes AI, support and continuous updates, positions Extreme Platform ONE Security as the first truly accessible NAC solution for organizations of all sizes
For decades, network access control was bolted onto existing infrastructure as an afterthought: add a Radius server here, a policy engine there, manage it separately from wireless, separately from wired. Extreme Platform ONE Security rejects this fragmentation. The solution is architecturally integrated from inception into the Extreme Platform ONE ecosystem, which unifies networking, security and AI.
How to position
Sell opportunities
- Bundle Infrastructure + Security: Position Platform ONE Security as a mandatory co-purchase with Extreme Fabric or Universal AP refreshes. Demonstrate ROI through reduced operational overhead and faster security deployment
- Emphasize Fabric + Security Convergence: Extreme's primary differentiator vs the competition is Extreme Fabric Connect. Highlight microsegmentation capabilities, stealth topology, and sub-second convergence as advantages that competitors cannot match. Bundle this with the Network Access Control capabilities using Platform ONE Security and you can deliver a highly performance wired network architecture fully cloud-driven.
- Highlight AI Automation: Extreme's AI Expert and AI Canvas are significant differentiators. Demonstrate in POC and discussions how conversational policy creation reduces complexity and accelerates deployments vs competitors' manual approaches
- Authorized Training Partner: Talk about the fact Kappa Data works as Authorized Training Partner for Extreme Networks and has a lot of knowledge and the ability to certify partners.
Microsoft Resellers & Entra ID Customers
The most immediately actionable positioning opportunity lies with Microsoft resellers and customers deploying Microsoft Entra ID. While Entra ID has become the de facto identity standard in hybrid enterprises, it has a critical functional gap: Entra ID lacks native cloud Network Access Control. Entra's Conditional Access Policies control access to Microsoft Cloud applications, but they do not control access to on-premises networks, wired connectivity, or wireless SSID assignment. This gap creates a natural upsell vetor.
When a Microsoft Entra customer needs to enforce zero-trust network access policies for their corporate WiFi, wired switches, and on-premises applications, they must turn to a third-party solution. Extreme Platform ONE Security fills this gap with pre-built, guided integration to Entra ID. A reseller can position the solution as the natural, seamless extension of an Entra ID deployment, offering the same identity-first, zero-trust philosophy that Entra provides for cloud apps, but now extending it to the physical network perimeter.
Microsoft Entra gives you identity-based access to cloud applications. Extreme Platform ONE Security extends that same identity engine to your network, so every device connecting to WiFi, wired or branch infrastructure follows the same zero-trust policies. One Engine. One Policy. One Dashboard
Typical Customer Profile:
- 50-5000 employees
- Hybrid cloud + on-premises infrastructure
- Recently migrated to Microsoft 365 / Entra ID
- Need modern, cloud-deliverd security without on-premises NAC complexity
- Limited IT security staffing
SME Mid-Market (Volume Opportunity)
Small and medium-sized enterprises represent 55.7% of the total enterprise NAC market revenue, yet they remain critically underserved. The barriers to NAC adoption for SMEs are well-documented: complexity of deployment, insufficient IT security expertise (only 28% have dedicated staff), high upfront capital expenditure for appliances, and the operational burden of managing traditional on-premises NAC solutions.
Extreme Platform ONE Security directly addresses these barriers through its cloud-first architecture and subscription-based pricing model (12 USD per user, covering up to 5 devices). Unlike on-premises NAC, which demands hardware procurement, appliance management, and specialized security talent, Extreme's cloud NAC requires minimal IT intervention: guided setup, automatic policy enforcement, and built-ins support.
Typical customer profile:
- 20-500 employees
- Growing IoT and BYOD adoption
- Limited on-premises IT infrastructure
- High vulnerability to cyber attacks
- Budget-conscious, prefer OpEx over CapEx
Extreme Hardware Installed Base
Organizations already running Extreme wired, wireless, or fabric infrastructure represent a straightforward upsell opportunity. Platform ONE Security integrates natively with Extreme hardware, enabling automatic configuration of NAC policies, SSIDs, ports, and VLANs. This removes friction from adoption and delivers immediate value to existing customers.
Educational Institutions & Distributed Enterprises
Extreme Platform ONE Security is pre-configured to support eduroam and manage identity-based access across multiple campuses and remote locations. Educational institutions with complex, multi-site deployments and high device density (students, contractors, guests) benefit from simplified workflows and centralized policy management
The NAC for Everyone
For small businesses, traditional NAC solutions are unattainable
- Cisco ISE: Requires 2-4 appliances, specialized security expertise, large upfront cost
- Aruba Clearpass: Similar cost + complexity profile
- On-premises NAC: High CapEx, high OpEx, resource-intensive management
Result: SMEs remain unprotected, relying on basic username/password authentication, leaving them vulnerable to BYOD compromise, IoT attacks, and insider threats
For mid-market enterprises, the choice is between:
- Expensive, complex on-premises NAC
- Emerging cloud NAC vendors with limited integrations
- Building a custom solution (months of integration work)
For large enterprises, options exist, but fragmentation persists:
- Multiple point solutions
- Inconsistent policies across access vectors (wired, wireless, remote, application)
- High operational overhead: separate teams managing separate systems
How Extreme Platform ONE Solves This:
"NAC for Everyone means:
- No CapEx Barrier: Cloud deployment eliminates hardware procurement. A 50-person company can deploy in hours; a 50.000-person company uses the same platform
- No Expertise Barrier: Guided setup, pre-integrated IdP/MDM connectors, and AI-driven automation eliminate the need for specialized security staff
- No Complexity Barrier: One policy engine replaces fragmented network, identity, and application access controls
- No Scale Barrier: Architecture scales from 50 users to 500.000+ without architectural change or license re-negotiation
- Inclusive Pricing: 12 USD per user per year (up to 5 devices) fits any budget.
Core Features
- Unified Identity-Based Policy Engine At its foundation, Extreme Platform ONE Security consolidates network access control and application access control into a single, identity-centric policy engine. Rather than managing fragmented policies across separate NAC, ZTNA, and firewall systems, IT teams define policies once based on user identity, device posture, and context: and the platform enforces them consistently across all access vectors: wireless, wired, branch, and remote.
A single policy might read: "Marketing staff devices must be compliant with Intune policies and pass endpoint assessment before connecting to corporate WiFi; they receive access to marketing-approved applications only" That policy is enforced identically whether the user is on campus, working home via ZTNA, or connecting to a branch office.
This unified approach eliminates the configuration drift, inconsistent enforcement, and operational blind spots that plague organizations running separate NAC and security solutions.
- Pre-Integrated Identity Provider & MDM Connectors Traditional NAC deployments require custom integrations with each identity provider and MDM platform, adding weeks to deployment timelines and introducing integration complexity. Extreme Platform ONE Security ships with pre-built, guided connectors to:
- Identity Providers: Microsoft Entra ID, Okta, Google Workspace
- Mobile Device Management: Microsoft Intune, Google Workspace
- Encryption Protocols: RADSec, RADIUS (via Radius proxy on-prem), IPSec & Wireguard (ZTNA)
These pre-integrations enable guided setup, administrators answer simple questions in a wizard, and the platform automatically configures policies, authentication flows, and device assessments. Organizations report deployment in hours, not weeks
- Automatic Device Configuration
When a new device dconnects to the network or a new location is added, traditional NAC requires manual configuraiton: defining port policies, creating VLANs, assigning authentication rules. Platform ONE Security automates this through integration with Switch Engine and Fabric switches and wireless access points.
New switches automatically adopt to Extreme Platform ONE Security, inherit security policies and begin enforcing network access without manual intervention. Wireless access points auto-provision with the correct SSIDs and security profiles. This "zero-touch" automation reduces operational overhead and accelerates network expansion while maintaining consistent security.
- AI-Powered Automation & Troubleshooting
Extreme Platform ONE includes conversational, multimodal and agentic AI that reduces manual configuration and accelerates troubleshooting. IT teams can describe policy intent in natural language ("Block guest devices from accessing file servers"), and the platform suggests policy rules. AI agents automate routine tasks like policy updates, device profiling, and compliance remediation.
For troubleshooting, the platform surfaces root-cause analysis, recommends remediation, and can execute automated responses (e.g. isolate a compromised device, trigger re-authentication, escalate to security team).
Feature Overview
Extreme Platform ONE Security implements industry-standard authentication mechanisms for both wired and wireless network access control. The platform supports three primary authentication methods:
- 802.1X EAP-TTLS: Provides tunneled EAP authentication, encrypting authentication credentials within a secure tunnel. This is suitable for environments requiring certificate-based security without the overhead of full certificate infrastructure on all endpoints
- 802.1X EAP-TLS: Delivers certificate-based authentication without tunneling, offering the strongest security posture. Every authentication transaction is cryptographically verified through client and server certificates, making this the preferred method for highly sensitive environments
- MAC Authentication Bypass (MAB) serves as a fallback authentication mechanism for devices that lack 802.1X supplicant capability (typically legacy endpoints, IoT devices, printers and IP phones). While less secure than 802.1X, MAB enables organizations to extend network access to non-compliant devices while maintaining segmentation through VLAN assignment.
All three authentication methods operate seamlessly on both wired (Ethernet) and wireless (WiFi) networks, with configuration managed through ExtremeCloud IQ or Extreme Platform ONE.
Policy Deployment & Dynamic VLAN Assignment
The core of Platform ONE Security's NAC capability lies in its identity-based policy engine, which assigns network access policies dynamically based on multiple contextual factors. Policies are deployed to network switches via dynamic ACLs (dACLs) conveyed through RADIUS vendor-specific attributes.
When a device authenticates to the network, the RADIUS server returns policy directives that instruct the switch to:
- Assign the device to a specific VLAN based on user role, department, or device type
- Apply rate limiting, traffic filtering, or isolation policies
- Trigger remediation workflows if the device fails compliance checks
Dynamic VLAN assignment operates on three logical triggers:
- Succesful authentication: Users authenticates with correct credentials --> assigned to production VLAN (e.g. "Sales" or "Engineering" segment)
- Authentication failure: User enters incorrect credentials --> assigned to quarantine VLAN with internet-only access
- Compliance violation: Device fails security posture assessment (missing antivirus, outdated OS patches, etc.) --> assigned to restricted VLAN, isolated from sensitive resources
This granular control eliminates manual port configuration while enforcing zero-trust principles: every device assignment is dynamically determined, never static.
Network Device Integration & Onboarding
Platform ONE Security supports enterprise-class Extreme Switching infrastructure:
- Supported Switches: 4120, 4220, 5320, 5420, 5520, 5720, 7520, 7720, X435
- Operating Systems: Fabric Engine 9.0.2+, Switch Engine 33.2.1+
The platform offers two deployment models for switch integration:
Managed Mode:
ExtremeCloud IQ / Platform ONE manages switch configuration and maintains centralized policy control. During onboarding, the system automatically provisions:
- RadSec certificates for secure communication to the cloud RADIUS server
- 802.1X or MAC authentication settings
- RADIUS/RadSec server configuration
- Instant Secure Port workflow: Converts standard switch ports into NAC-enabled ports that enforce authentication policies
Policy updates from Platform ONE Security are automatically distributed to managed switches as dynamic ACLs, requiring no manual intervention.
Locally Managed Mode:
Switches are onboarded to Platform ONE but retain local configuration control. The switch must be manually configured to:
- Connet to the cloud RadSec server via native RadSec (newer Extreme switches only) OR
- Route authentication requests through a local RadSec Proxy for compatibility with non-RadSec-capable devices
This hybrid approach accomodates organizations with strict on-premises control requirements or legacy infrastructure constraints.
RadSec Proxy & Secure RADIUS Transport
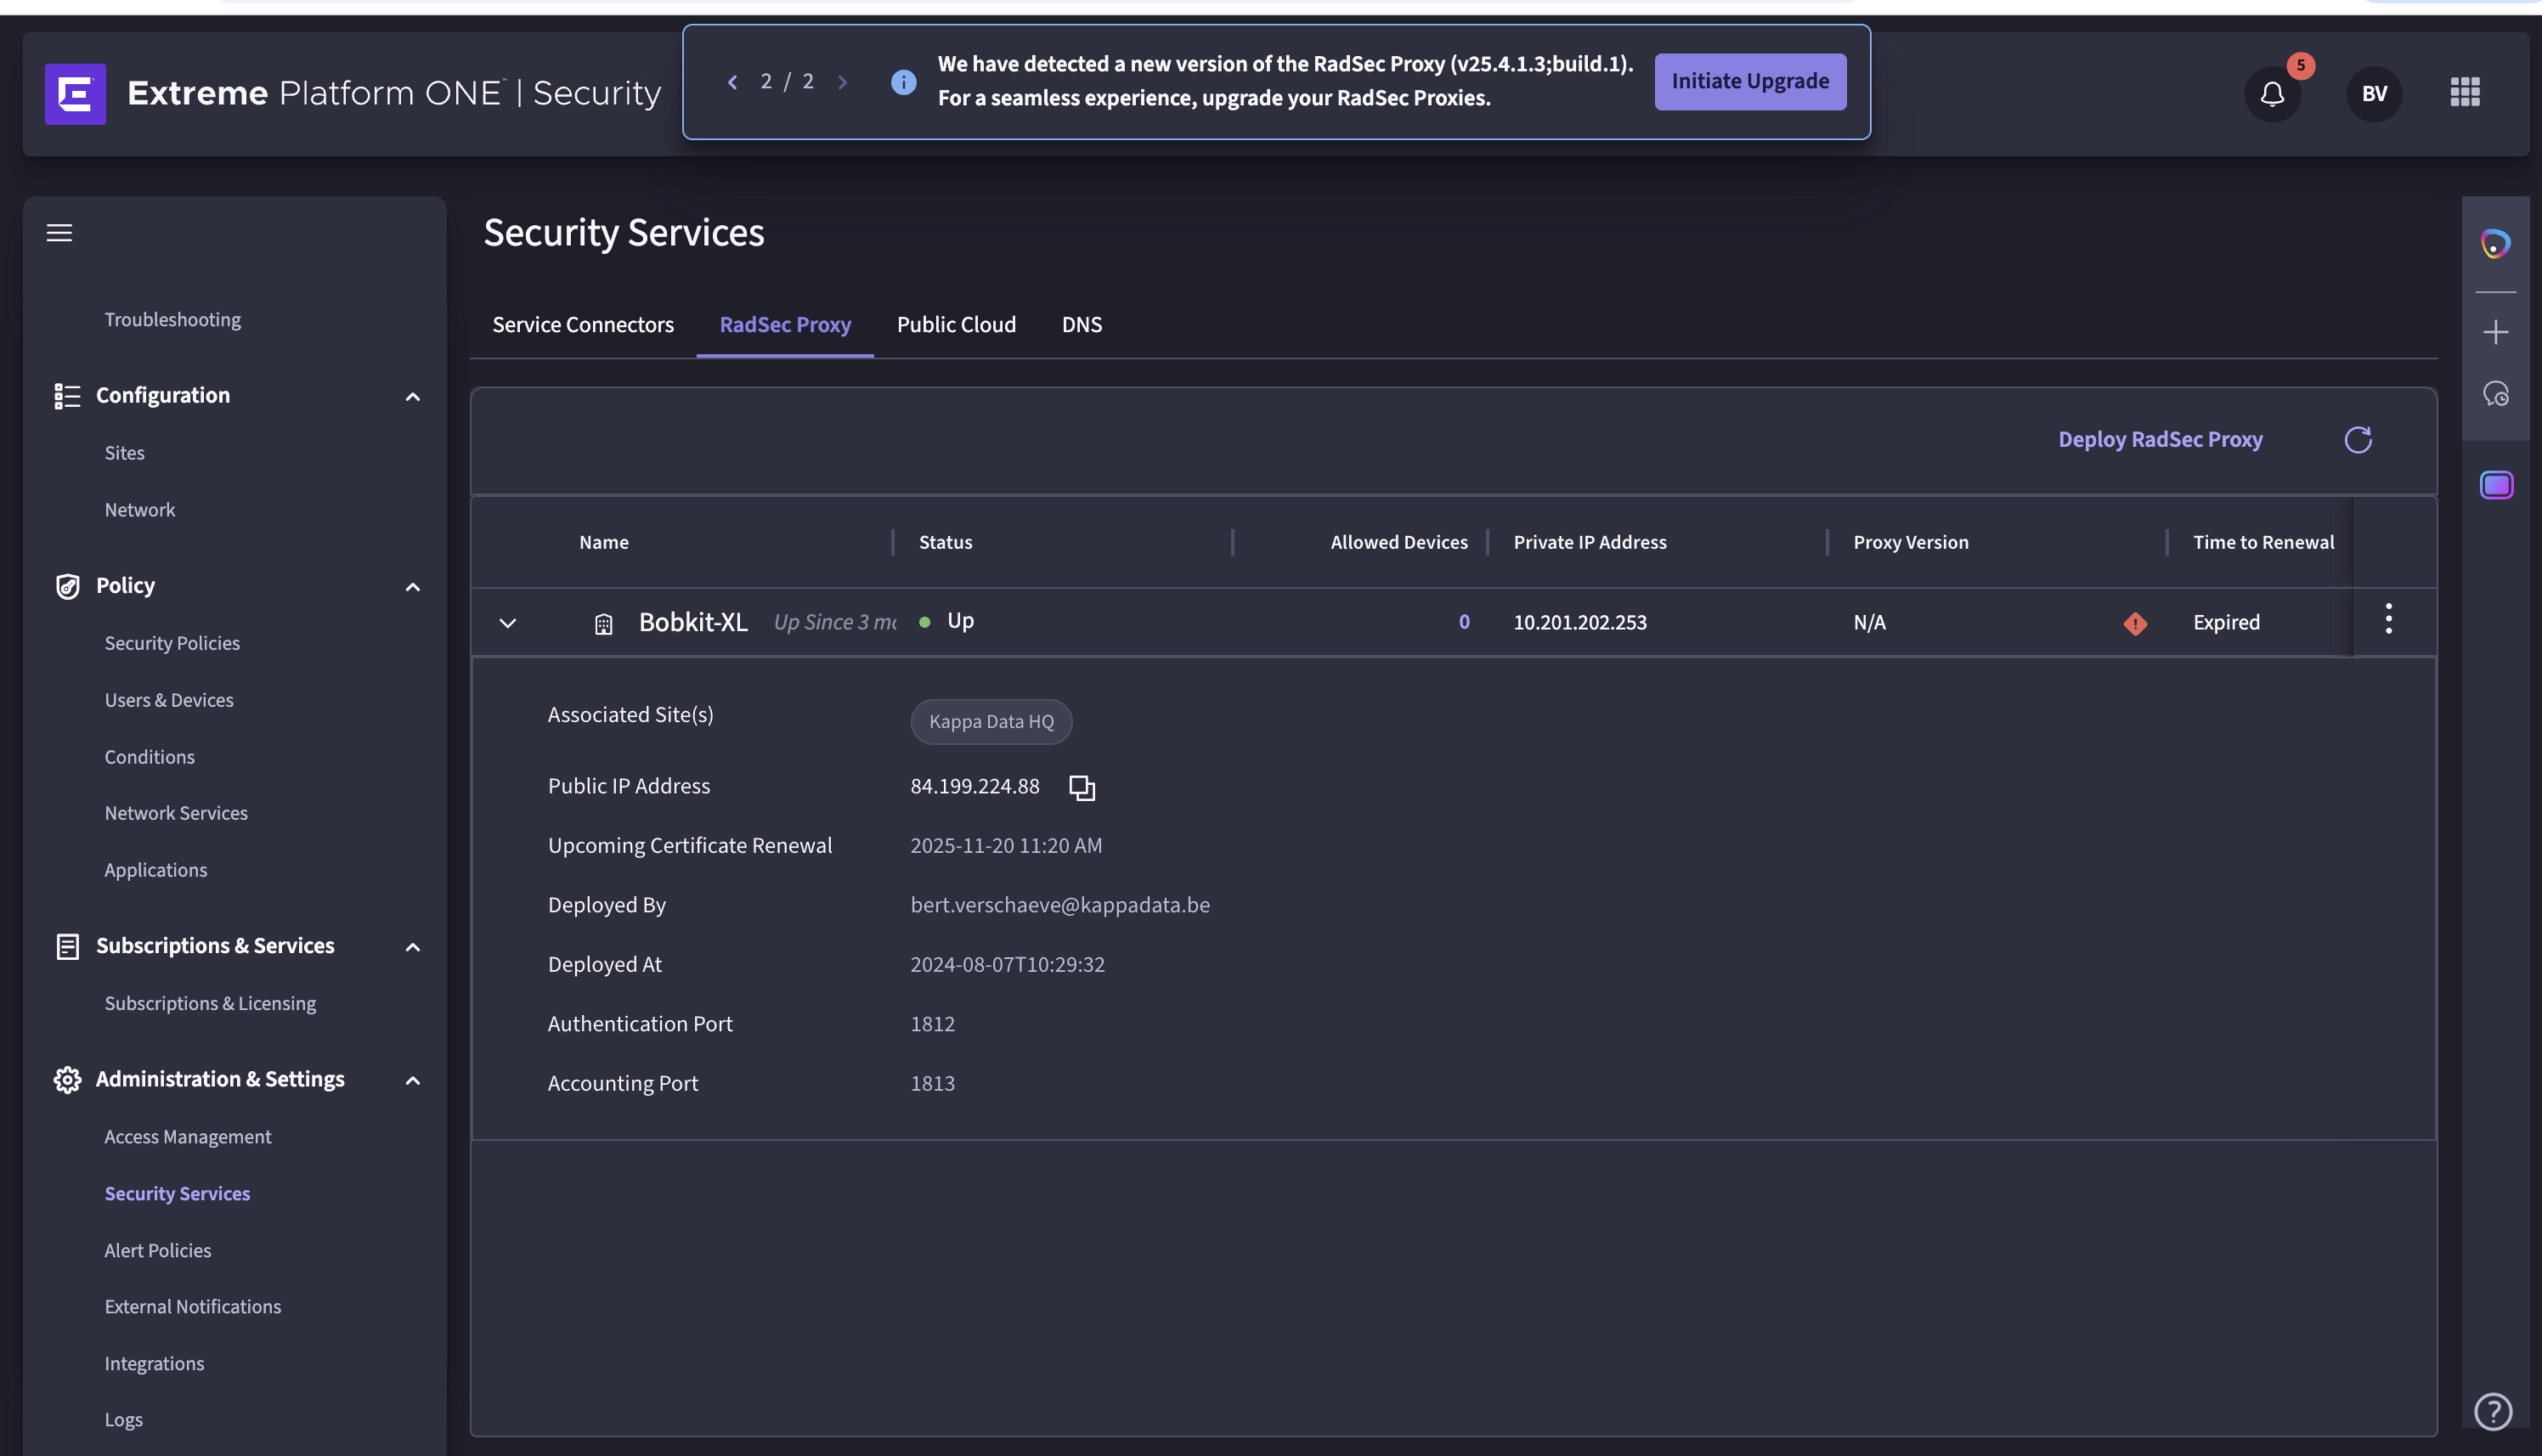
The RadSec Proxy addresses a critical security gap in traditional NAC deployments: unencrypted RADIUS traffic traversing untrusted networks (internet-facing, cloud-connected). Platform ONE Security implements RFC 6614 RadSec (RADIUS over TLS) to encrypt all authentication traffic:
Architecture:
- Older switches or third-party switches unable to support native RadSec send unencrypted RADIUS authentication requests to a local RadSec Proxy
- The RadSec Proxy establishes a TLS-encrypted tunnel to ExtremeCloud
- Authentication request is forwarded over the encrypted tunnel to the cloud RADIUS server
- Authentication response is returned over the same TLS tunnel back to the RadSec Proxy
- RadSec Proxy forwards response to the switch in standard RADIUS format
Key Capabilities:
- RadSec Proxy is deployed on-premises (customer's datacenter or branch office)
- Operates independently; does not require direct cloud connectivity from switches
- Supports multiple RADIUS realms for multi-tenant or multi-site deployments
- Automatic failover between multiple proxy instances for redundancy
This architecture enables organizations to extend cloud NAC to legacy switches, third-party infrastructure (Cisco, Aruba, HP), and distributed branch offices without requiring native cloud connectivity at each access layer.
Extreme Networks is known to deliver vendor-agnostic, third-party friendly solutions. With Extreme Platform ONE Security you are able to sell an affordable NAC solution that integrates with all third-party network infrastructure vendors.
Identity Provider Integration
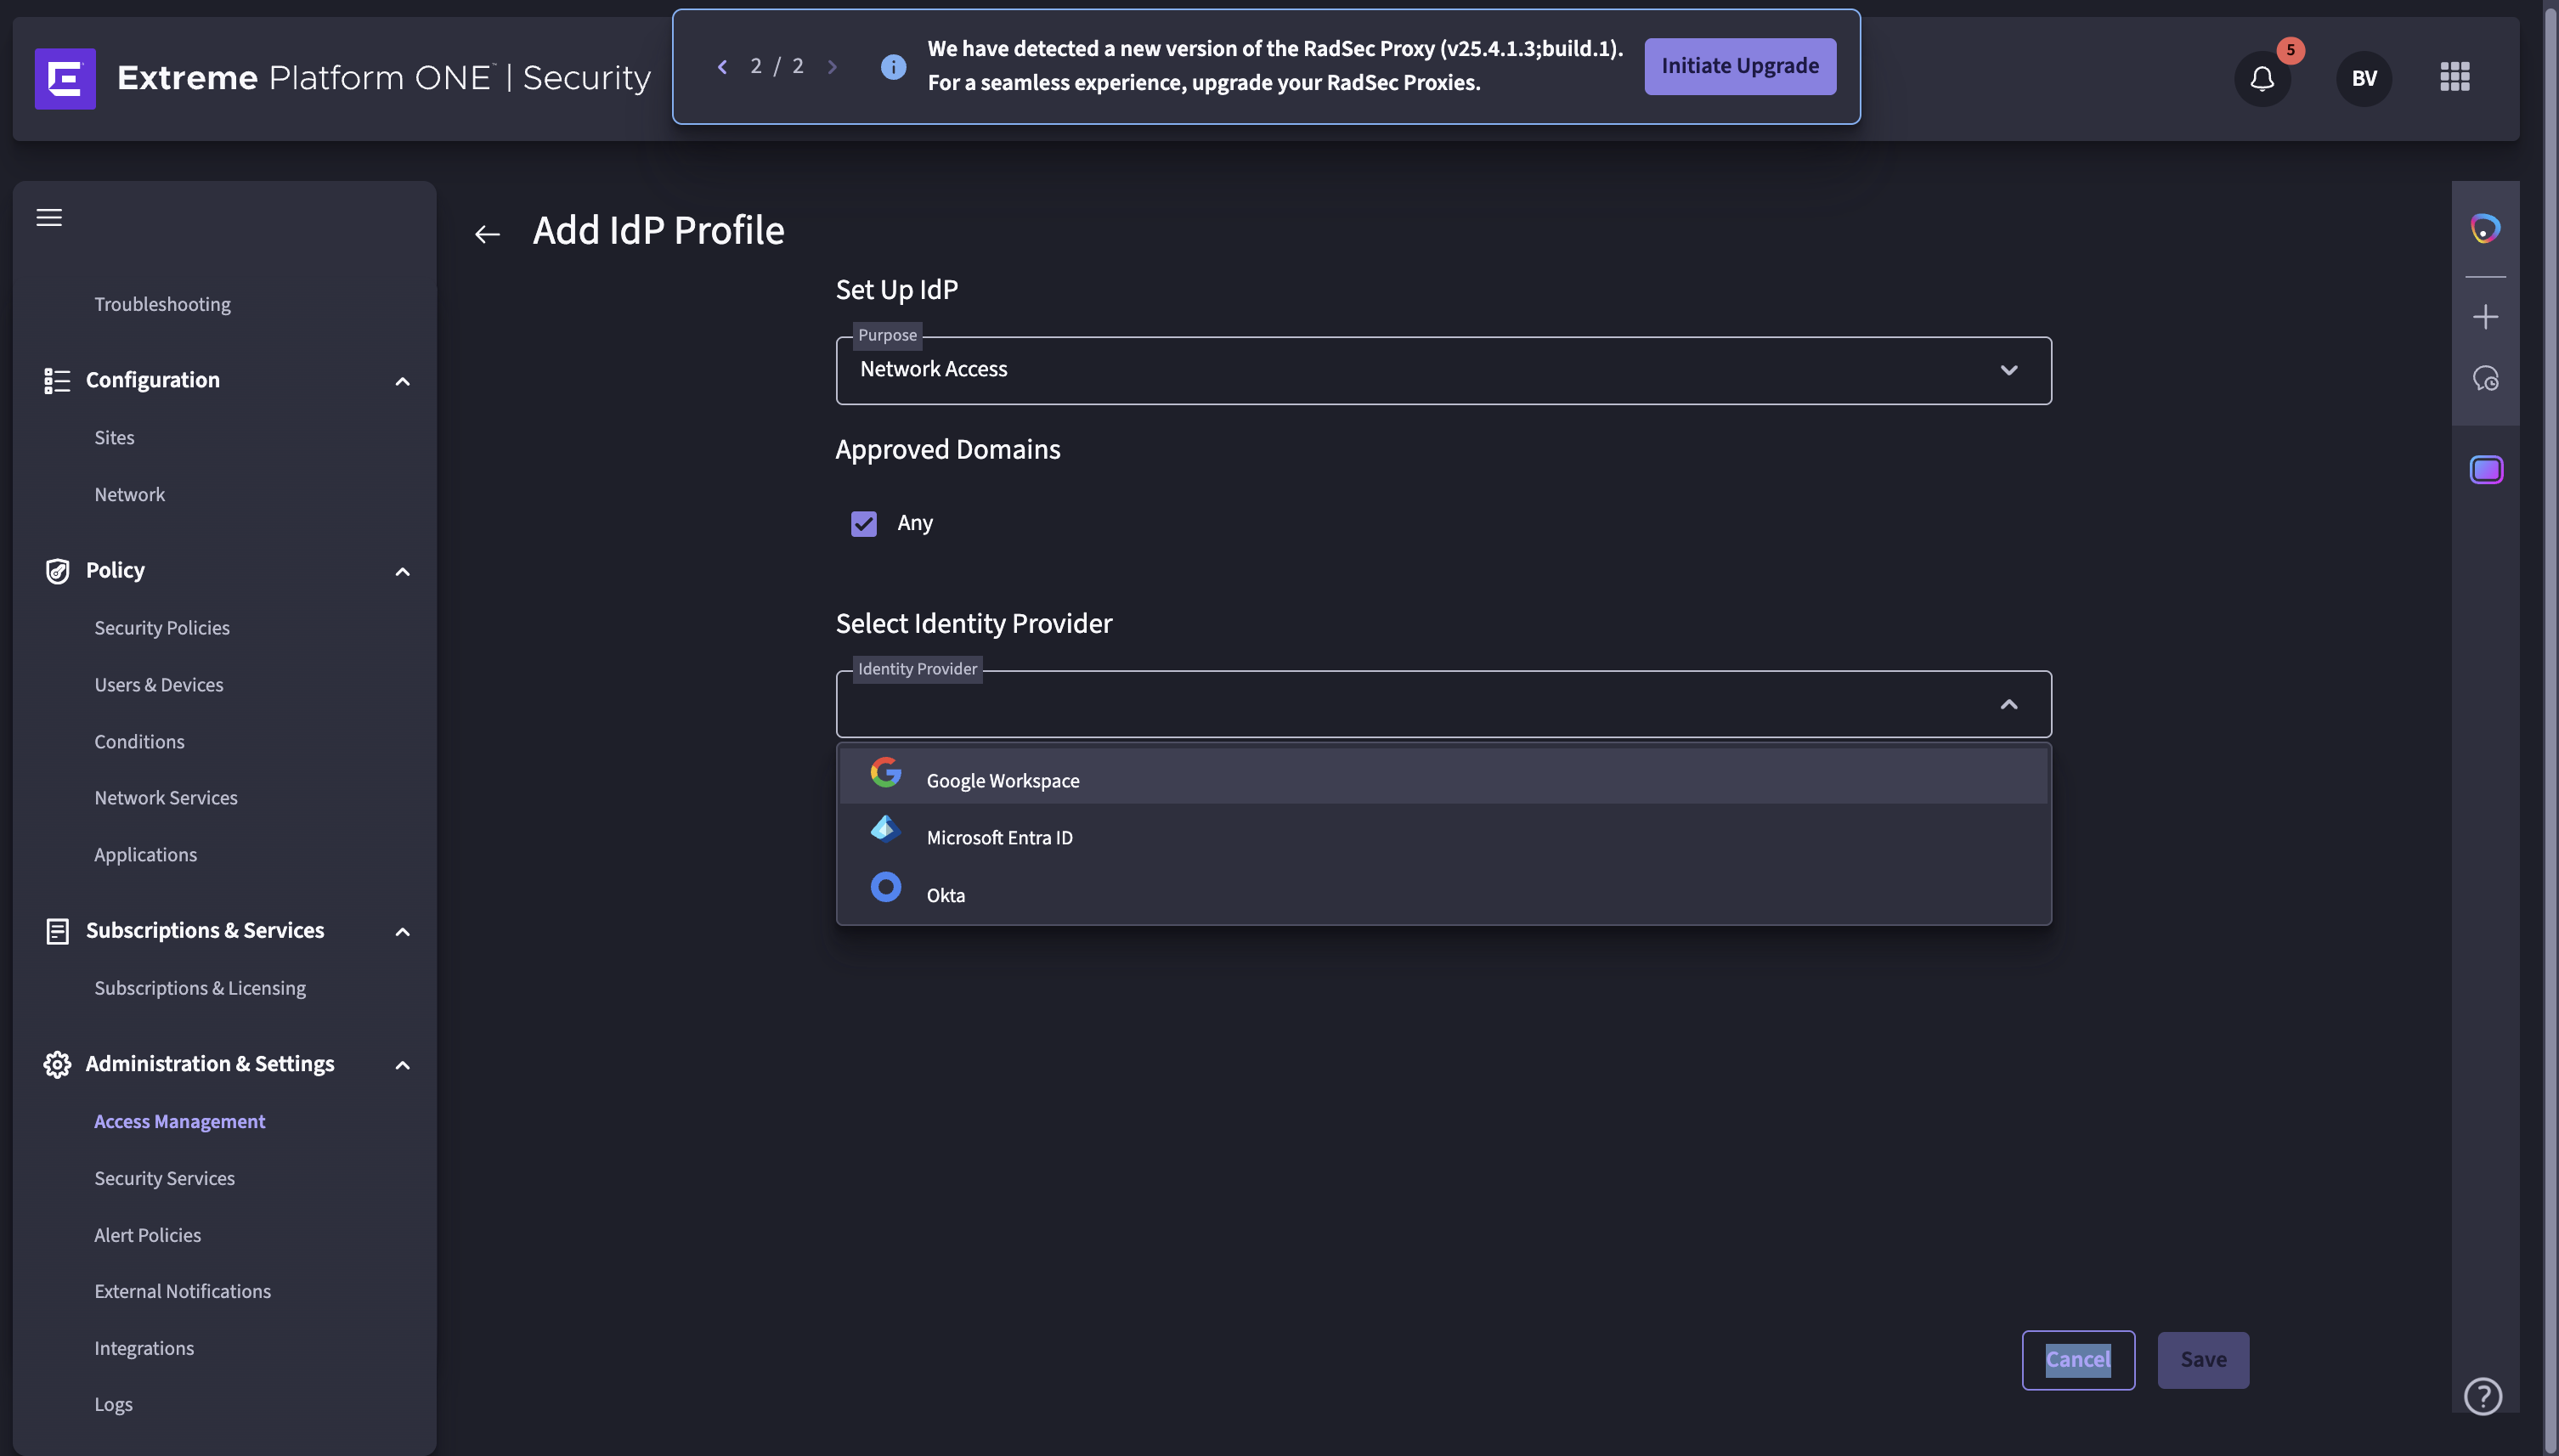
Platform ONE Security integrates with leading enterprise identity platforms, enabling role-based access control and single sign-on (SSO) capabilities
Supported Identity Providers:
- Microsoft Entra ID
- Okta
- Google Workspace
Entra ID Integration Details
When Microsoft Entra ID is configured as the identity provider:
- Group-based policy assignment: Users in Entra groups automatically receive corresponding network policies (e.g. marketing@kappadata.be group --> Marketing VLAN + Internet-only firewall policy)
- OIDC for application access: OpenID Connect enables single sign-on to applications with IdP setup completed in Entra ID first and then replicated in Platform ONE Security
- Real-time access revocation: When a user is deprovisioned in Entra ID, their active network sessions are terminated immediately; all certificates are revoked.
Microsoft Intune Integration
Platform ONE Security deeply integrates with Microsoft Intune MDM to enforce cevice compliance as a prerequisite for network access.
Real-time compliance checking
- Platform ONE Security queris Intune's compliance status in real time during 802.1X authentication
- Only devices passing Intune compliance baseline receive network access
- Devices failing compliance checks are automatically assigned to quarantine VLAN
Supported compliance checks
- Operating system version and patch level
- Antivirus status (active, up-to-date definitions)
- Firewall enabled
- Disk encryption enabled (BitLocker, FileVault etc)
- Windows Defender/Microsoft Defender status
- Custom compliance policies defined in Intune
AI-Powered Policy Management & Automation
Platform ONE Security includes AI Expert, an agentic AI system that simplifies policy creation and optimization.
Natural Language Policy Creation
Instead of manually navigating policy configuration interfaces, administrators can describe policy intent conversatioinally
- Example: "Give John access to the ERP application"
- System Response: AI interprets intent, identifies relevant groups, and suggests policy rule
AI-assisted recommendations are applied in clicks, reducing policy creation time from hours to minutes
Policy Validation & Optimization
The AI engine:
- Analyzes existing policies for security gaps or misconfigurations
- Identifies policies that conflict with zero)trust principles
- Recommends optimizations (consoldiate overlapping rules, tighten overly permissive rules, etc)
- Flags compliance violations (e.g. This policy grants guest access to production VLAN)
Security Guardrails
Extreme implements robust safeguards against AI hallucinations and adversarial attacks:
- Hallucination detection: Identifies and mitigates AI-generated false recommendations
- Prompt injection prevention: Detects and blocks adversarial input attempting to manipulate AI behavior
- Harmful content detection: Blocks malicious or inappropriate outputs
- Reinforcement learning: AI model continuously improves through human feedback
All customer data sent to AI models for training is anonymized and PII-stripped; only non-identifying feedback is retained for model improvement
Monitoring, Analytics & Audit
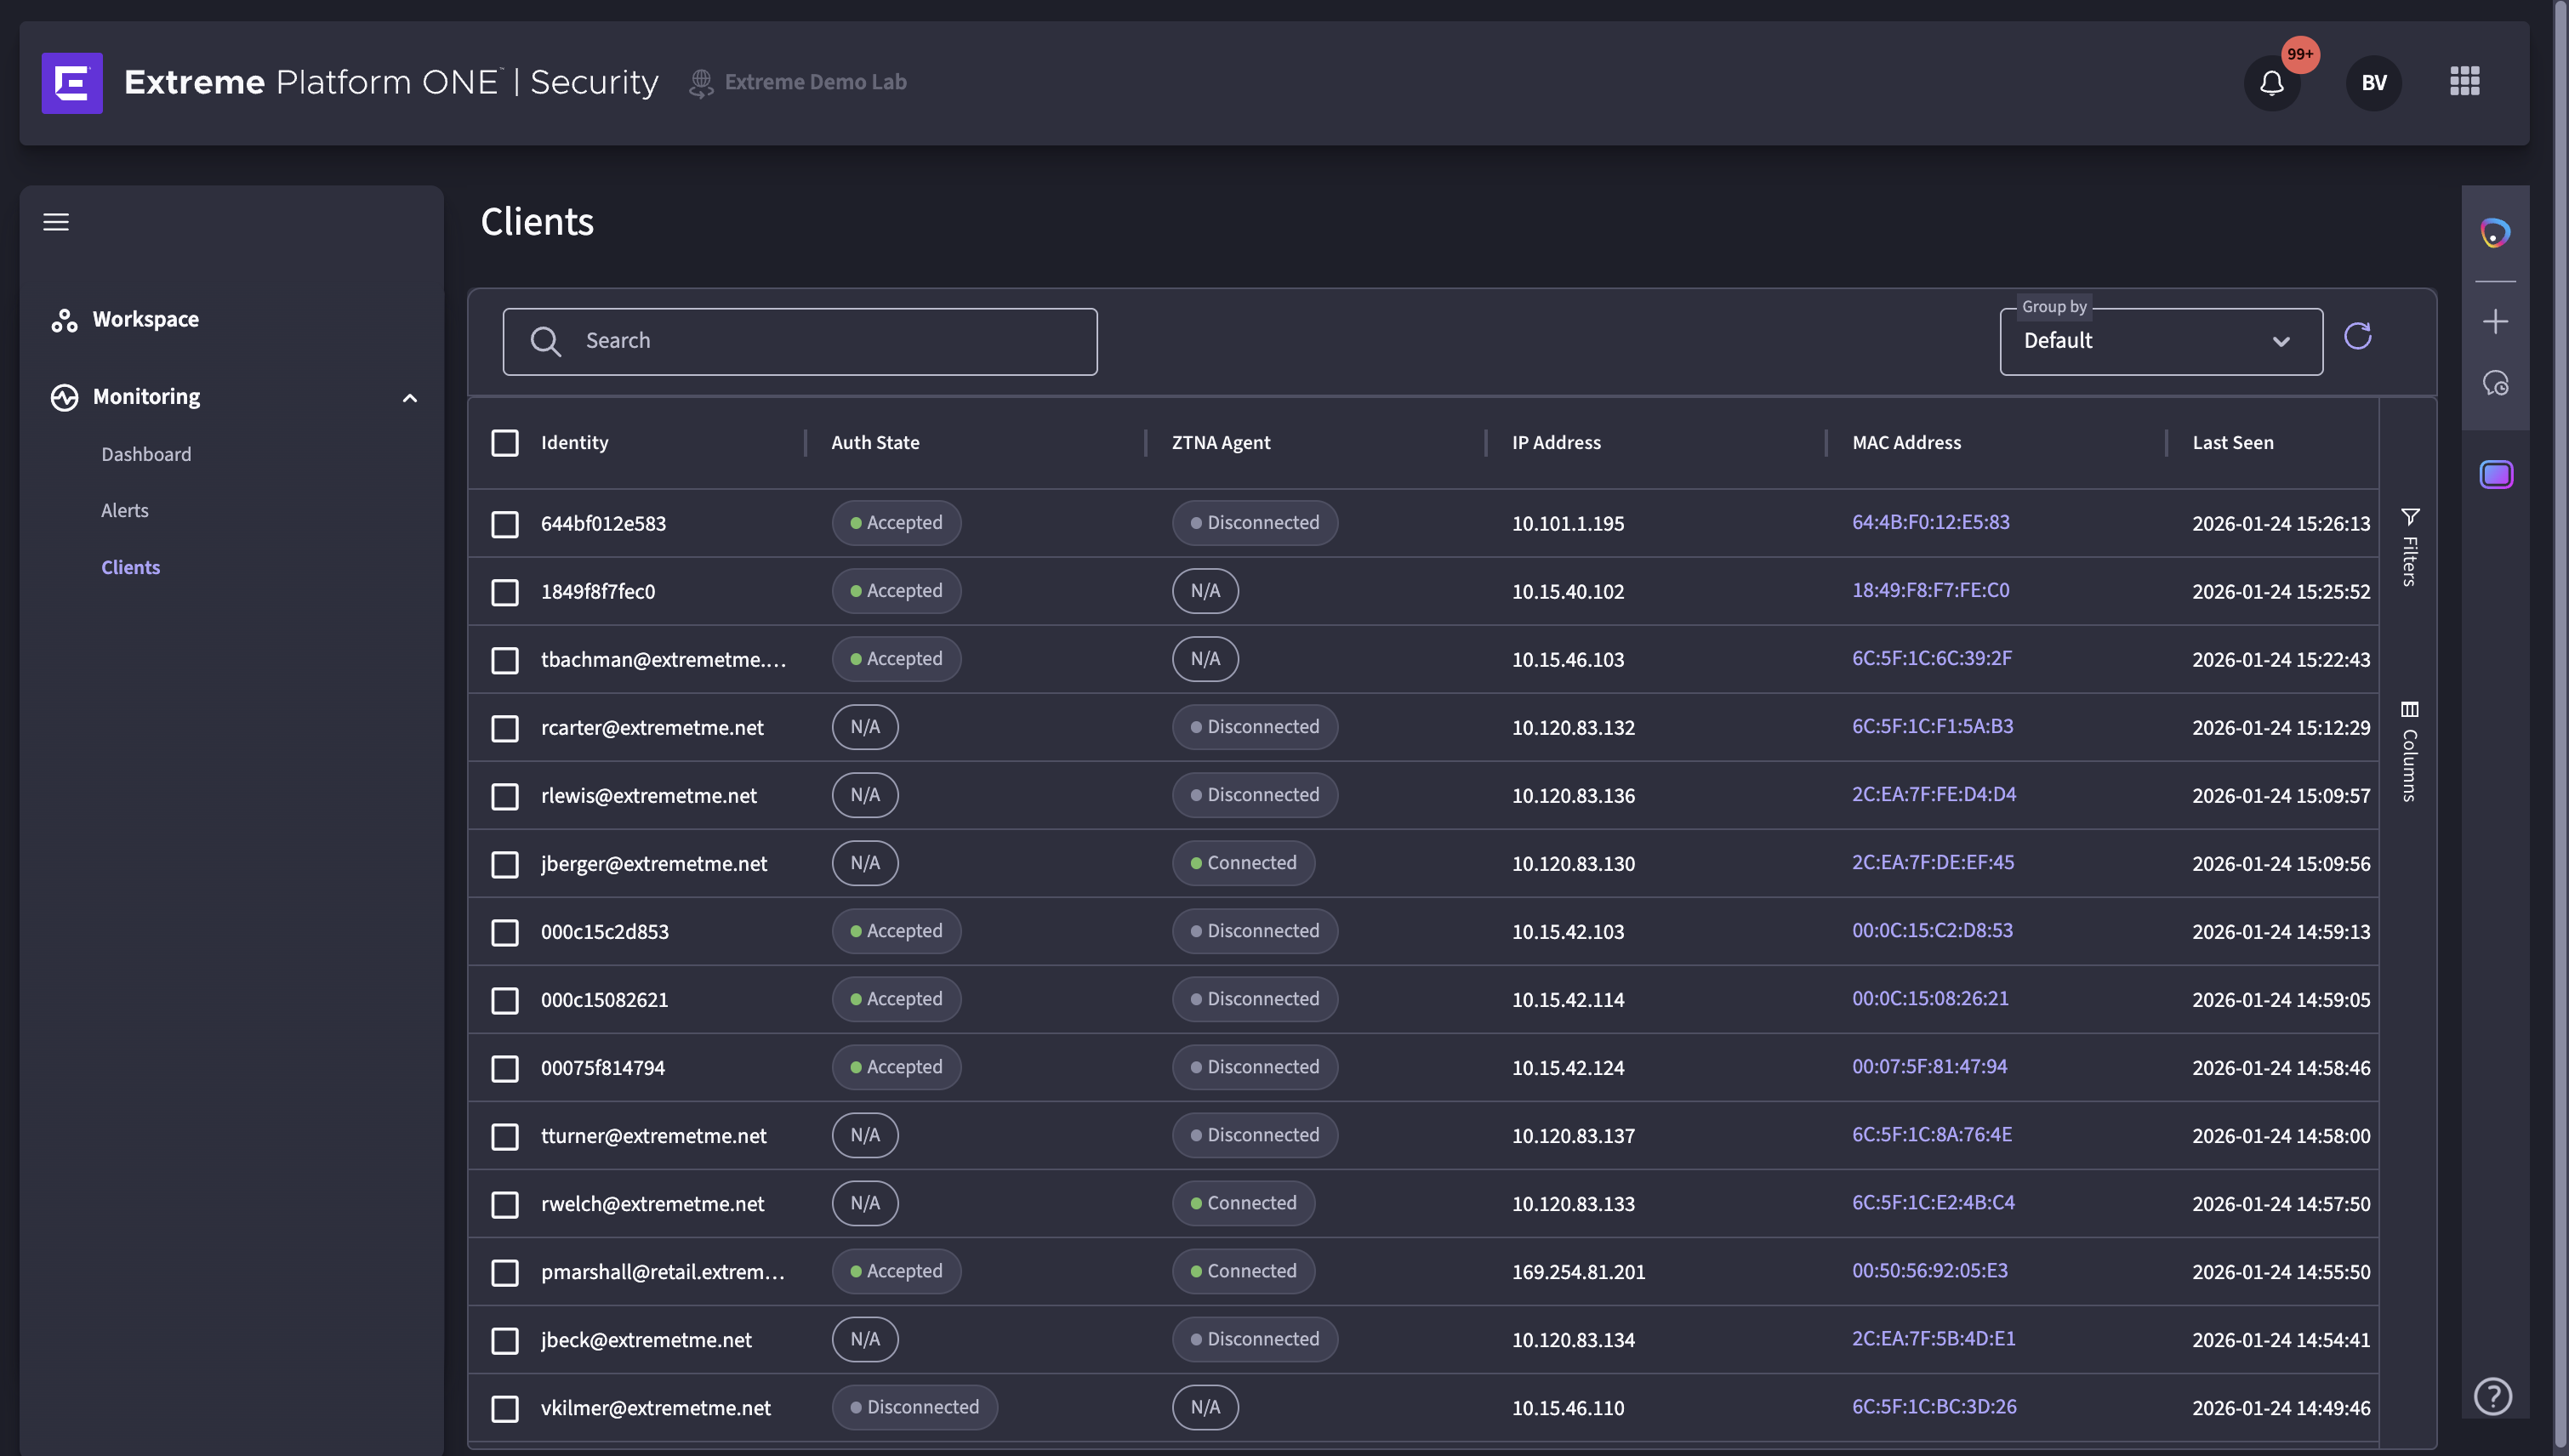
Platform ONE Security provides comprehensive visibility into network access and device posture across all deployment models.
Unified Monitoring Dashboard
- Multi-domain, multi-layer views: Single login provides visibility across wired access, wireless access, remote access (ZTNA), and application access
- Geo maps and topology views: Visualize assets from global down to individual policies and devices
- Real-time health and alerts: Device status, client connectivity health, authentication failures, compliance violations
- Device inventory: Asset planning and compliance tracking at a glance
IP-to-ID Mapping
Platform ONE Security creates a persistent mapping of:
- User identity
- Device hostname
- IP address
- MAC address
- Connection location (switch port, AP SSID)
- Timestamp of authentication
This mapping is critical for forensic investigation (answering "Who accessed which resources?") and compliance auditing
Audit Logs
- All access decisions logged with timestamp, user, device, policy applied
- Simplifies compliance audits and change monitoring
- Enables forensic investigation of security incidents
- Supports rollback of policy changes
Conclusion
Extreme Platform ONE Security represents the first truly democratized NAC solution, enabling organizations of any size to deploy enterprise-grade network access control without the complexity, cost, or expertise barriers of traditional solutions. By unifying cloud NAC, ZTNA, identity, device management, and network infrastructure under a single AI-driven platform, and by shipping pre-integrated connectors to Microsoft Entra ID, Okta, and Google Workspace, Extreme has positioned itself at the intersection of three critical market trends:
- The explosive growth of cloud-first deployments,
- The shift from VPN to ZTNA/NAC
- The urgent need for security solutions SMEs can actually implement.
The most immediate market opportunity lies with Microsoft resellers and Entra ID customers—a massive installed base that today lacks network-level access control. The secondary opportunity is the underserved SME segment, where 55.7% of NAC market revenue sits locked away by cost and complexity barriers. By positioning Platform ONE Security as "the NAC for everyone," Extreme can capture significant share across these segments while maintaining credibility in enterprise deployments.